

2025 Cybersecurity Year in Review
December 2025 | Enterprise Threat Recap
Executive Summary
2025 was the year attackers stopped knocking on doors and started walking through open windows. The numbers tell a brutal story: $10.5 trillion in global damages, 4,701 ransomware incidents in nine months, and an average 5-month dwell time before anyone noticed intruders in their network.
But the real lessons aren't in the stats—they're in the tradecraft. A 17-year-old social engineered his way past UK retail giants by calling the help desk. Lazarus Group poisoned a developer's Docker project and walked away with $1.5B in crypto. Clop hit 335 victims in a single month by targeting file transfer software nobody remembered to patch. And a manufacturing breach at JLR cascaded into £1.9B in economic damage across 5,000 suppliers who thought they weren't the target.
If you're reading this thinking "we have security tools for that"—so did they. This report breaks down what actually happened, what the attackers exploited, and what your team should be doing differently. No vendor pitches, no checkbox compliance. Just the operational reality of what threat actors are doing right now.
2025 By the Numbers
Before diving into individual cases, here's the macro picture. These aren't projections—they're confirmed incidents from the past 12 months:
4,701 ransomware incidents from January through September—a 34% jump from last year. That's roughly 17 organizations getting hit every single day. Insurance carriers are raising premiums and tightening coverage, but the attacks keep coming faster than the industry can adapt.
192.7 million healthcare records confirmed stolen, with Change Healthcare alone accounting for most of that number. Healthcare remains the most targeted sector because patient data fetches premium prices and hospitals can't afford downtime.
16 billion credentials found circulating on dark web markets and Telegram channels. Password reuse is still the easiest entry point for most attackers. If your organization isn't monitoring for credential exposure, you're flying blind.
335 victims in February alone from Clop's Cleo campaign. One threat group, one vulnerability class, one month. That's what mass exploitation looks like when defenders are slow to patch file transfer software.
$200M+ in deepfake fraud losses just in Q1. The Arup case showed that a single video call with AI-generated executives can authorize a $25M wire transfer. Voice and video verification are no longer reliable.
2025 Timeline: Month-by-Month
January 2025: Ivanti Zero-Day — They Were Inside Before Anyone Knew
The year started with a gut punch. CVE-2025-0282 in Ivanti Connect Secure VPN appliances (CVSS 9.0) was being exploited in the wild weeks before Ivanti even knew about it. By the time the advisory dropped, multiple U.S. federal agencies were already compromised.
This is textbook nation-state tradecraft. UNC5337, a suspected China-nexus group, was running the campaign. They scanned for internet-facing Ivanti appliances, dropped crafted requests to trigger pre-auth RCE, and immediately deployed webshells for persistence. From there, the VPN gateway became their pivot point into internal networks. CISA issued Emergency Directive 25-01—the urgency was real.
Here's what makes this particularly nasty: your VPN is supposed to be the security perimeter. When attackers own it, they're not breaking through your firewall—they are the firewall. Every downstream control becomes irrelevant. And because VPN appliances often run proprietary OS stacks, traditional EDR doesn't see what's happening on them.
The hard truth: If you're running edge devices that you can't monitor with your existing security stack, you're trusting the vendor's security posture entirely. Ivanti has had multiple critical vulns over the past two years (CVE-2023-46805, CVE-2024-21887). At some point, you have to ask whether the attack surface is worth it.
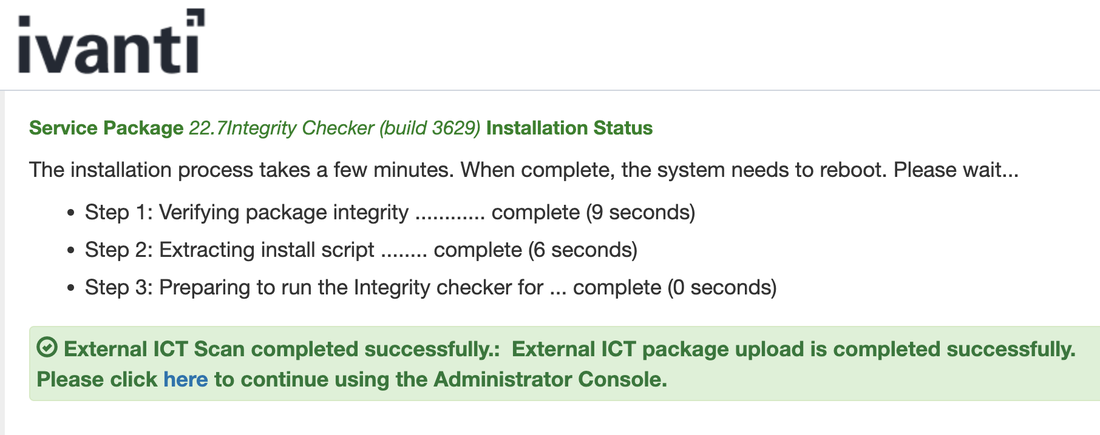
What to do: Run Ivanti's Integrity Checker on all appliances—not tomorrow, today. Review VPN logs for anomalous connection patterns. Long-term, start treating your VPN as an untrusted asset. Zero Trust isn't a buzzword here; it's the recognition that perimeter devices get owned and you need to contain the blast radius.
February 2025: Bybit Heist — $1.5 Billion Gone in a Single Transaction
This one will be studied for years. Lazarus Group (DPRK's state-sponsored cybercrime unit, also tracked as TraderTraitor) pulled off the largest cryptocurrency theft in history—not by cracking encryption or exploiting a smart contract bug, but by compromising a single developer's laptop.
The attack started with a social engineering lure: a fake "stock simulator" Docker project sent to a Safe{Wallet} developer. Once the developer ran it, their MacBook was owned. From there, Lazarus extracted AWS credentials and used them to poison JavaScript files on app.safe.global—the web interface millions of users trust to sign transactions.
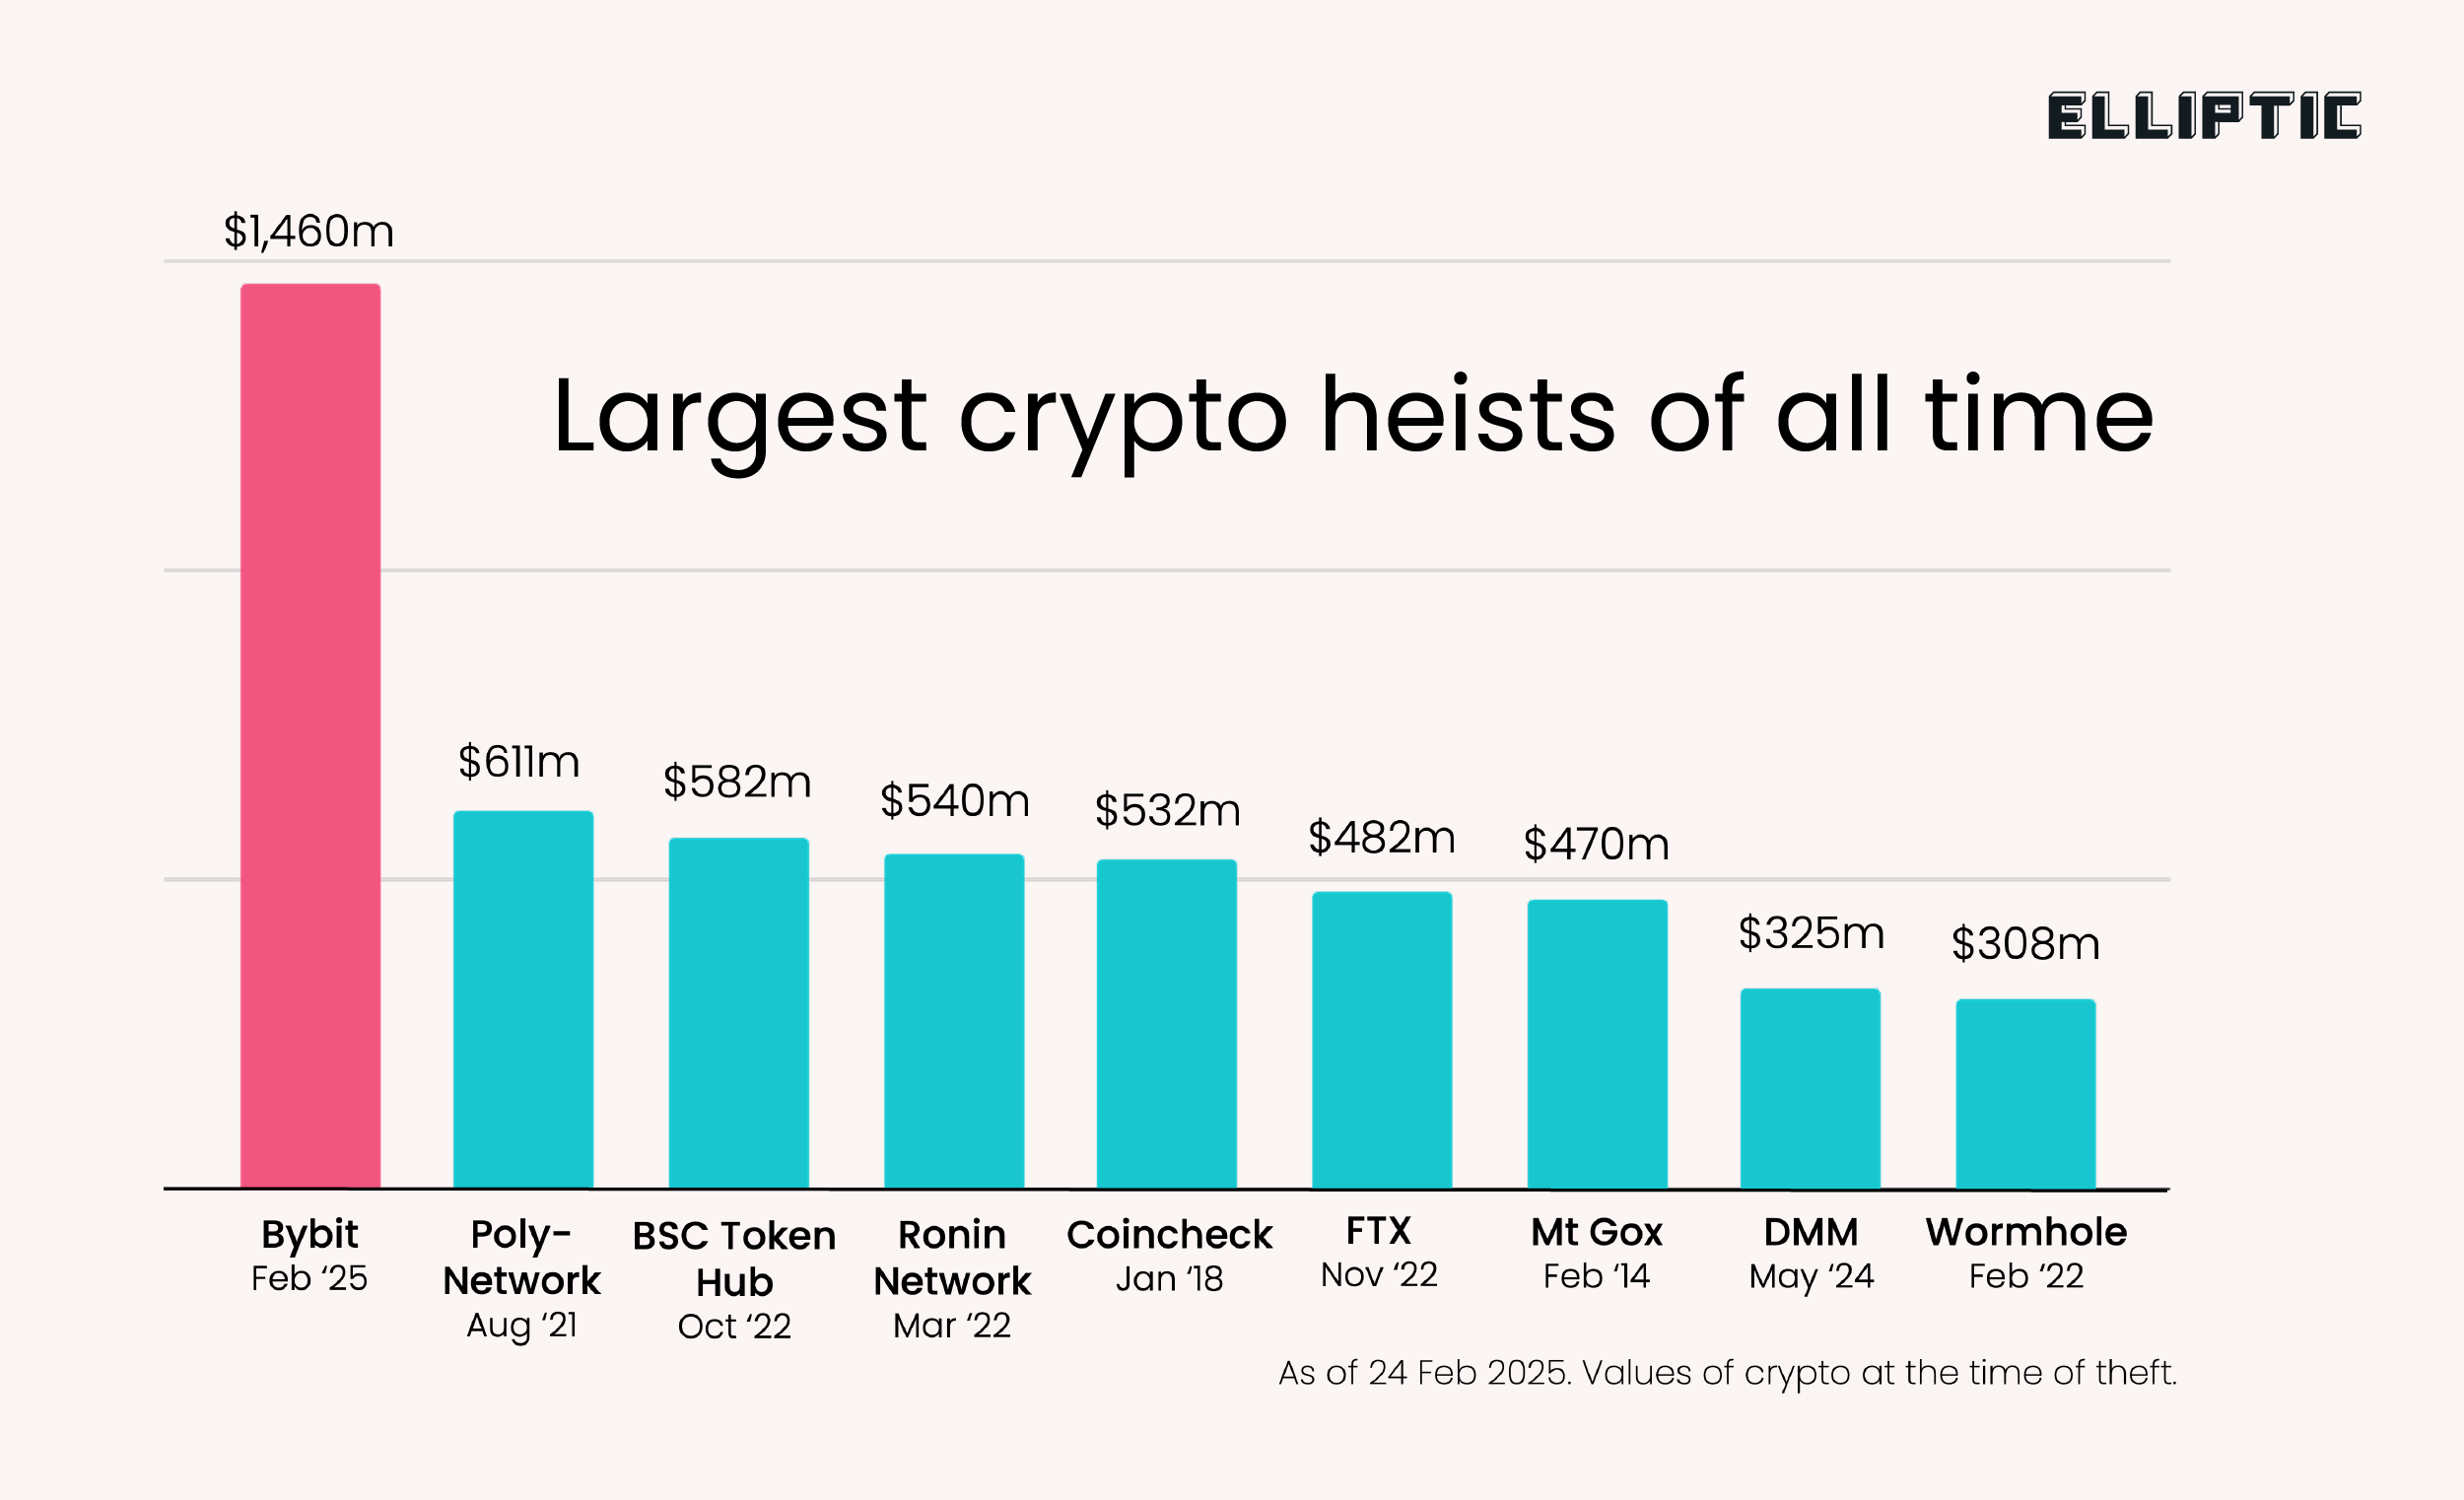
Here's the clever part: the malicious code specifically checked if the signer was Bybit's cold wallet. If yes, it silently swapped the destination address in the transaction while displaying the correct address in the UI. Every signer looked at their screen, saw a legitimate transfer to Bybit's hot wallet, and approved it. What they actually signed sent $1.5B to Lazarus-controlled wallets.
Multi-signature security didn't fail—it was completely bypassed. The attackers didn't need to compromise multiple signers. They compromised the interface those signers trusted.
Attack Flow
Within 5 days, over $400M was laundered through DEXs, cross-chain bridges, and Tornado Cash. The FBI formally attributed the attack to Lazarus in a public advisory. The remaining funds are being tracked, but for practical purposes, that money is gone. (NCC Group analysis)
The lesson here is uncomfortable: cryptographic security is only as good as the software presenting it. Hardware wallets would have caught this because they display the actual transaction data on a separate, air-gapped screen. But most enterprise crypto operations use web interfaces because they're convenient. That convenience cost Bybit $1.5 billion.
What to do: Developer workstations with access to production infrastructure need isolation—no random Docker projects, strict EDR, download restrictions. For high-value transactions, verify destination addresses through an independent channel. If you're managing significant crypto assets, hardware wallet verification isn't optional.
February 2025: UK Retail Attacks — A Phone Call That Cost £500M
This attack should terrify every CISO reading this report. Scattered Spider—a group whose members are literally teenagers—called M&S's third-party help desk, pretended to be a locked-out employee, and got a password reset. That's it. No malware, no zero-day, no sophisticated exploit. Just a convincing phone call.
From that single credential, they moved laterally to the domain controller, grabbed the NTDS.dit file containing every password hash in the domain, and spent two months cracking them offline while nobody noticed. When they had domain admin, they deployed DragonForce ransomware across VMware ESXi hosts, taking down M&S, Co-op, and Harrods in a coordinated strike.
Here's what's infuriating: the attackers were monitoring the incident response team's calls. They knew what defenders were doing and adjusted in real-time. That's the level of operational security from a group of 17-19 year olds.
Attack Flow
The financial damage was staggering: M&S lost £300M+ in direct costs plus a £500M stock drop. Co-op took a £206M revenue hit and had 6.5M customer records stolen. Harrods hasn't disclosed full impact. Combined, over £500M in damage from a single social engineering call. (BleepingComputer)
DragonForce, the ransomware-as-a-service platform, offers affiliates 80% profit share. That business model means anyone with basic social engineering skills can become a serious threat actor. The barrier to entry is now essentially zero.
What needs to change: Your third-party help desk is not your help desk—it's an attack surface. Implement callback verification to a registered phone number for any password reset. Protect your NTDS.dit with tiered admin accounts and Credential Guard. Segment your ESXi infrastructure so ransomware can't move laterally to hypervisors. And for incident response, assume attackers are listening—use out-of-band communication that they can't intercept.
February 2025: Clop's Cleo Campaign — 335 Victims in 30 Days
Clop has turned mass exploitation into an art form. Their February campaign targeting Cleo file transfer products (Harmony, VLTrader, LexiCom) hit 335 organizations in a single month—the most concentrated ransomware campaign we've ever documented.
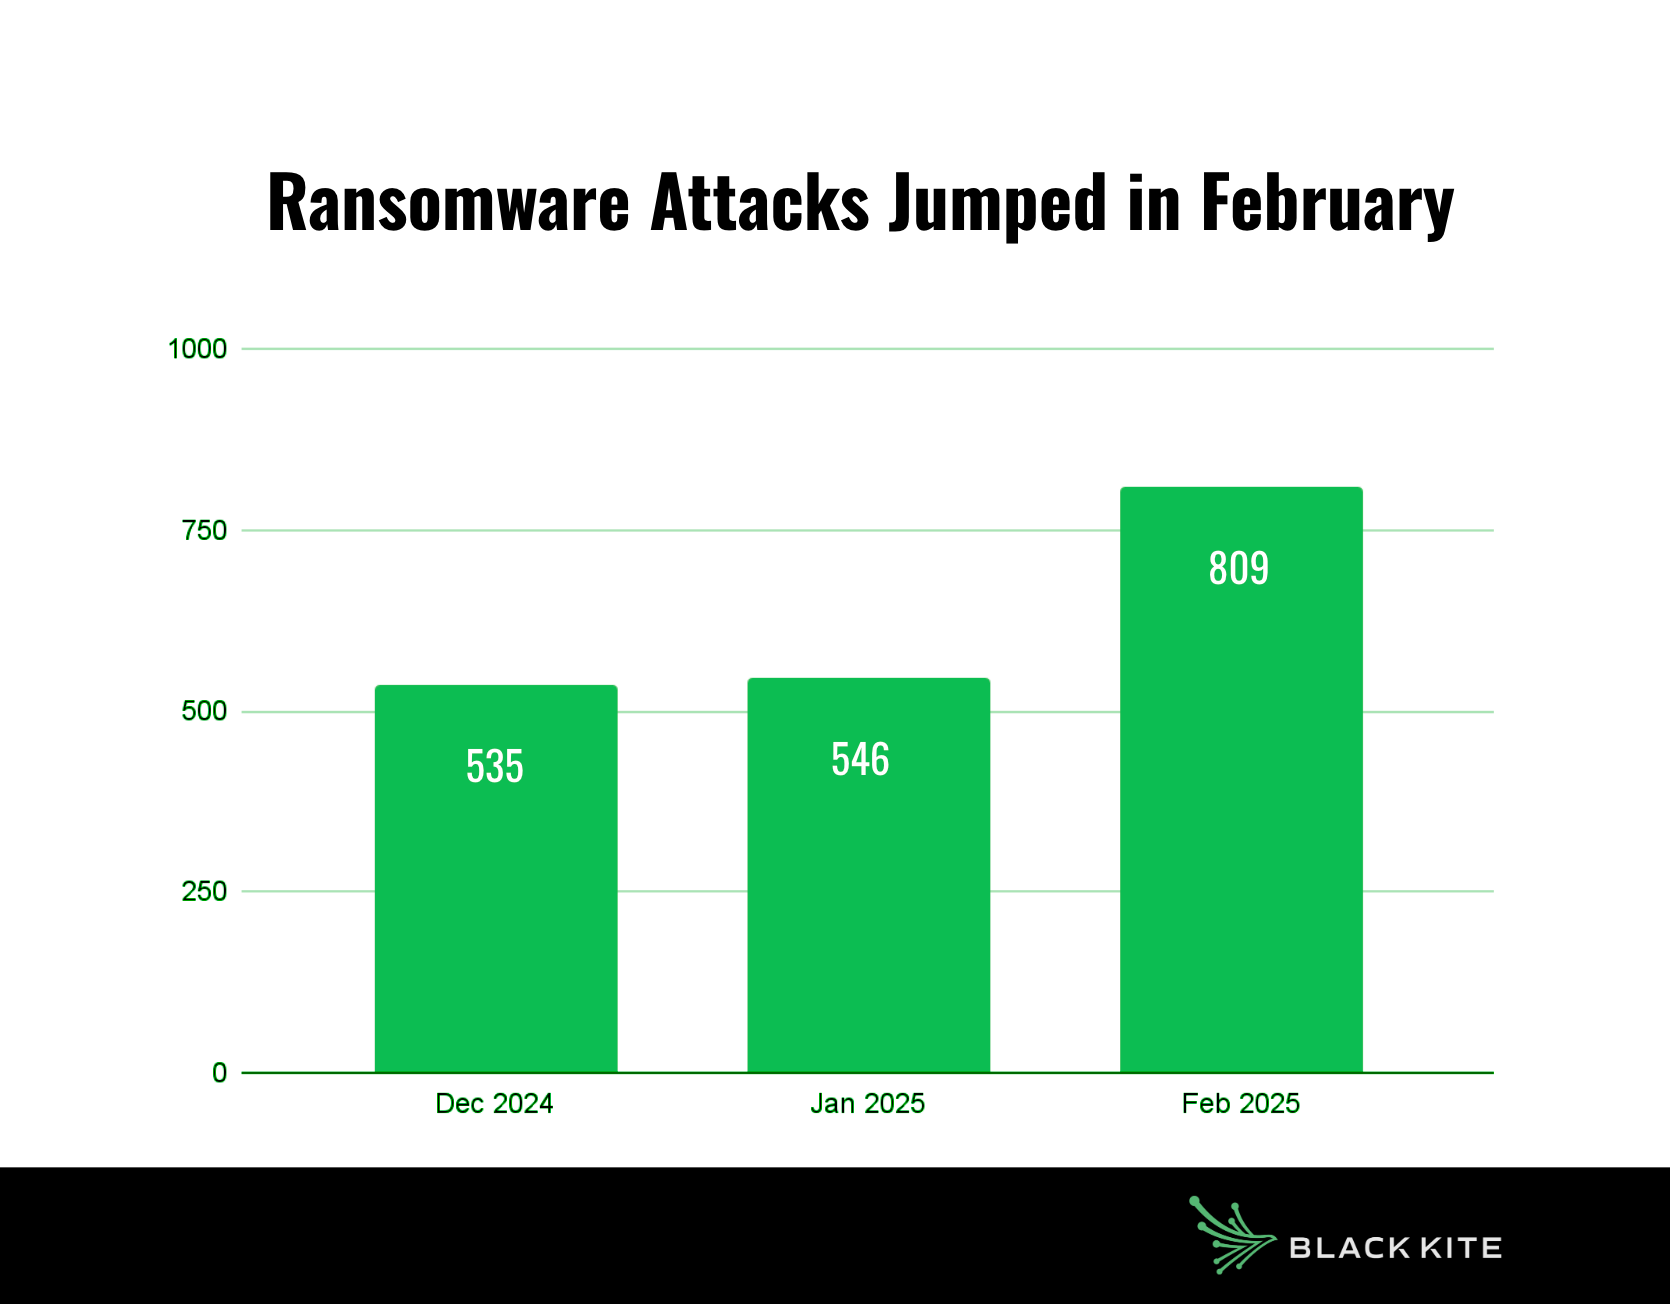
The playbook is now depressingly familiar. Clop finds a zero-day in widely-deployed file transfer software, scans the internet for exposed instances, drops webshells through unauthenticated RCE (CVE-2024-55956, CVSS 9.8), and exfiltrates data at scale. They don't even bother encrypting anymore—pure data extortion. Pay up or your files get published.
This is the third time Clop has run this exact play: MOVEit Transfer in 2023 (2,500+ victims), GoAnywhere MFT later that year (130+ victims), and now Cleo. Each campaign exploits the same pattern: managed file transfer solutions that enterprises deploy, expose to the internet for B2B data exchange, and then forget about.
Manufacturing took the hardest hit this time—28% of victims. Retail, healthcare, financial services, and logistics rounded out the target list. Every organization running B2B file transfers became a potential target overnight.
The uncomfortable reality: most security teams don't even have a complete inventory of their file transfer solutions. Shadow IT deployed a Cleo instance five years ago for a vendor integration, nobody documented it, and now you're on Clop's leak site. If you haven't audited your MFT footprint, do it today—not because of Cleo specifically, but because Clop will find another vendor next year. Patch to version 5.8.0.24 or later, put these systems behind a firewall, and monitor them like they're crown jewels—because to attackers, they are.
March 2025: GitHub Actions Compromised — 23,000 Repos Owned
The tj-actions/changed-files action had over 23,000 repositories depending on it. One compromised maintainer token later, every single one of those repos was running malicious code in their CI/CD pipelines.
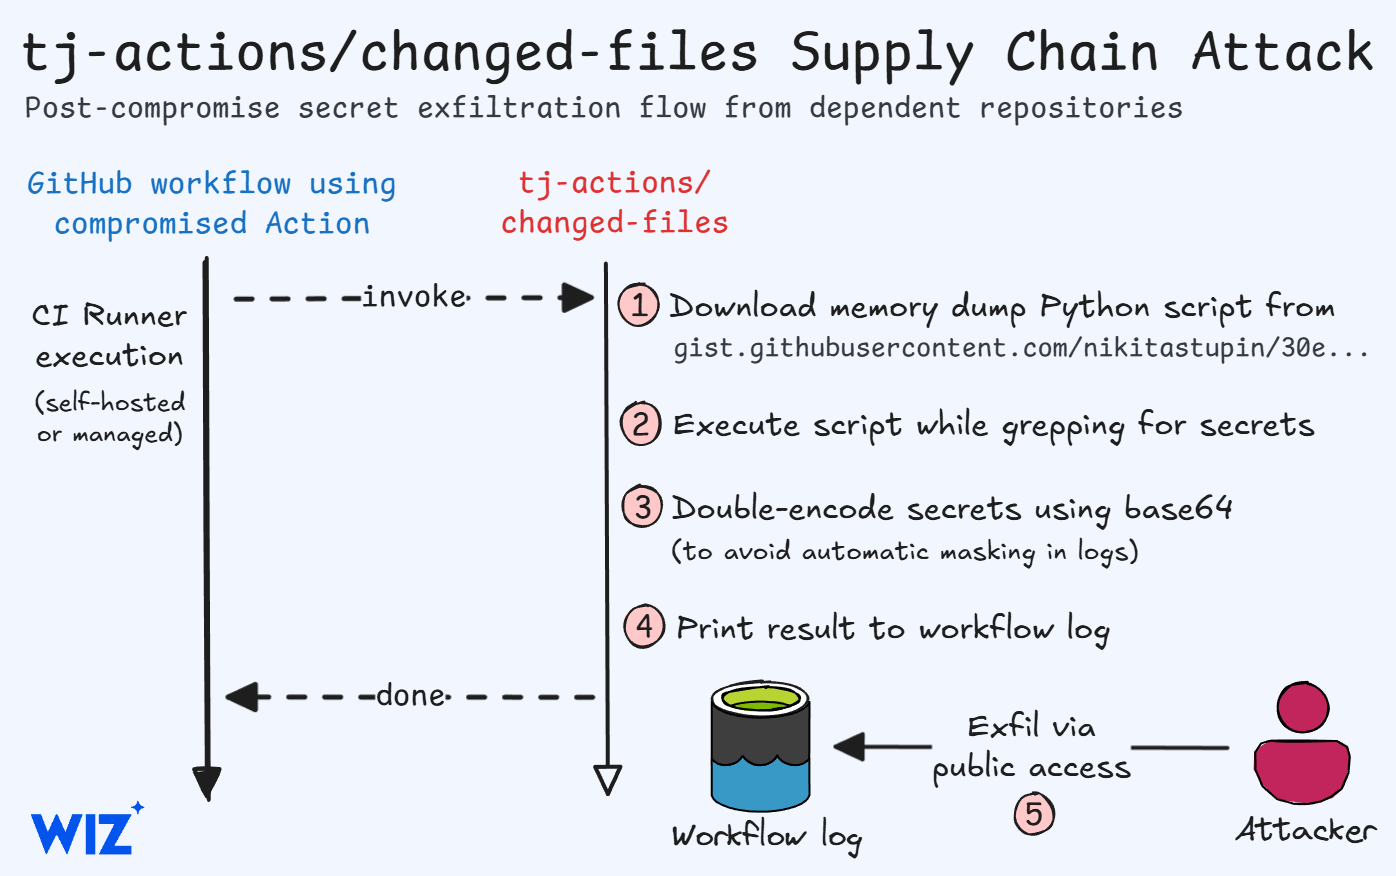
The attacker pushed a commit that dumped all environment variables—including secrets—to workflow logs. Then they updated the version tags so any workflow referencing @v4 would pull the poisoned version. AWS keys, npm publish tokens, GitHub PATs, deployment credentials—all of it exfiltrated to attacker-controlled infrastructure.
This is the fundamental problem with GitHub Actions' security model: version tags are mutable. When you reference actions/checkout@v4, you're trusting that the maintainer will never push malicious code to that tag. That trust was misplaced here, and 23,000 repos paid the price.
The fix is simple but annoying: pin every action to a specific commit SHA. Tags can be overwritten; commit hashes can't.
# VULNERABLE - tag can be updated to malicious code
- uses: tj-actions/changed-files@v4
# SECURE - immutable commit reference
- uses: tj-actions/changed-files@abc123def456
If you were running this action during the compromise window, assume your secrets are burned. Rotate everything that was accessible to your CI/CD pipelines—and consider implementing an allowlist for approved actions so developers can't casually add new dependencies without security review.
March 2025: Oracle Cloud Breach — When Your Provider Gets Owned
Here's a scenario that should keep you up at night: your cloud provider—the one you trust with authentication, SSO, and LDAP—gets breached. That's exactly what happened when a threat actor exploited Oracle Cloud's login infrastructure and walked away with 6 million records spanning 140,000+ tenants.
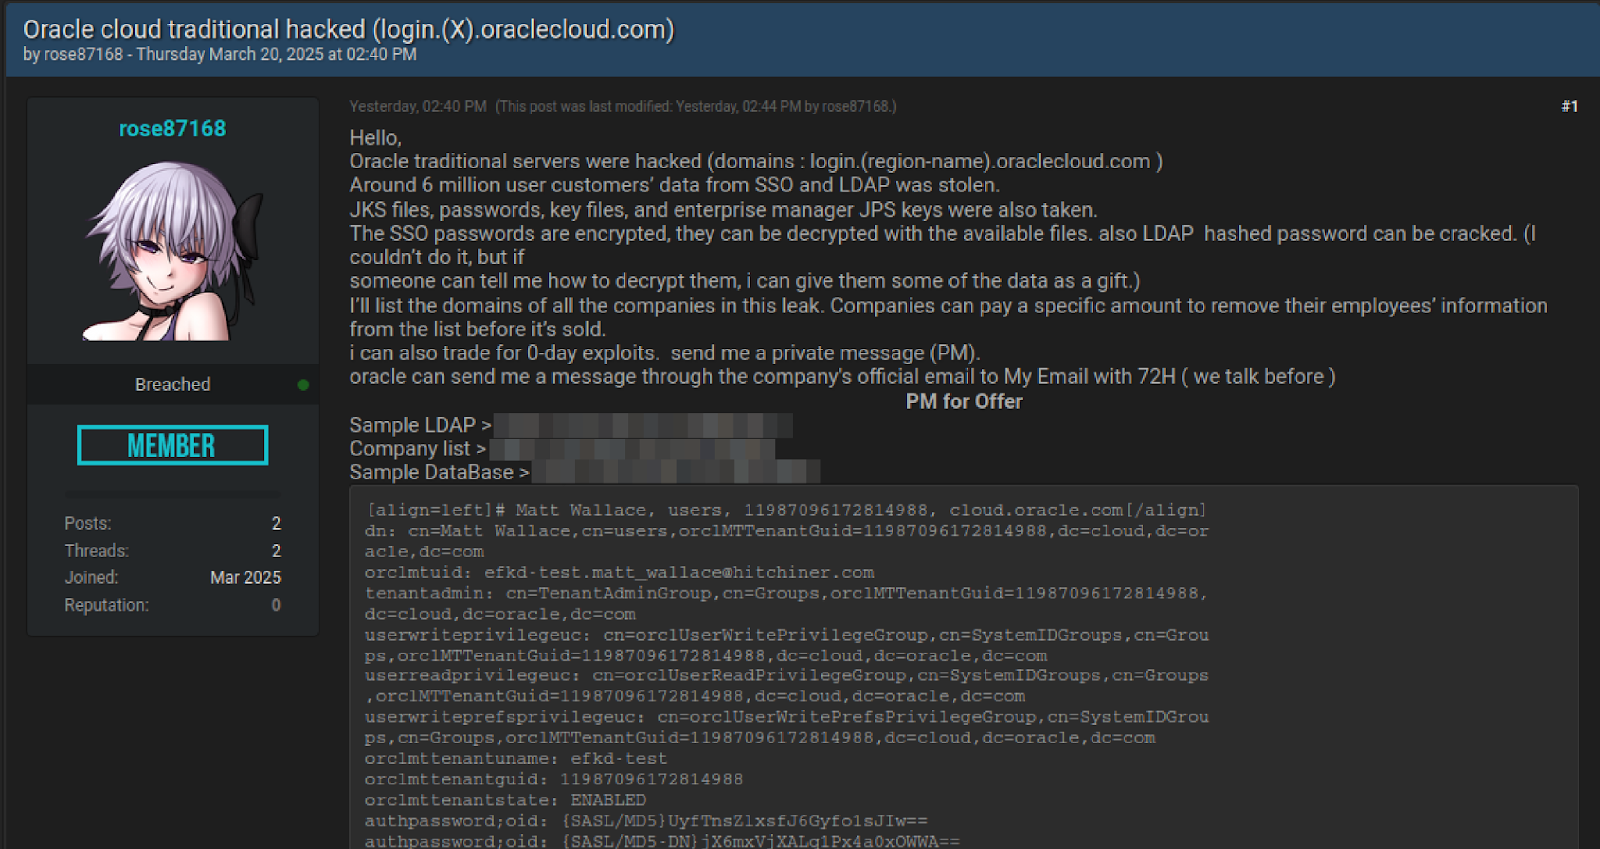
The haul included JKS files (Java KeyStore containing certificates), encrypted SSO and LDAP passwords, tenant configuration data, and LDAP connection strings. "Encrypted" sounds reassuring until you realize most of these hashes are crackable offline with enough GPU time. If an attacker has your encrypted credentials and motivation, consider them compromised.
This breach illustrates a blind spot in most security programs: you can't audit your cloud provider's security posture. You're trusting Oracle (or AWS, or Azure, or Google) to not get owned. When they do, every tenant gets hit simultaneously. There's no isolation, no containment—just mass exposure.
What to do: Force a password reset for all Oracle Cloud users, rotate SSO tokens, regenerate any certificates that were stored in the affected systems. If you haven't already enabled MFA on all accounts, this is your wake-up call. And monitor for credential stuffing attacks—those leaked credentials will end up in attack lists.
April 2025: SAP NetWeaver Zero-Day — Nation-State Actors Already Inside
CVE-2025-31324 is a perfect 10.0 CVSS score—missing authorization plus unrestricted file upload in SAP NetWeaver Visual Composer. By the time SAP disclosed it on April 24, Chinese APT groups had been exploiting it for over a month. We're looking at 581+ confirmed compromises across manufacturing, energy, and government sectors worldwide.
The timeline tells the story: reconnaissance scans started in late January, first exploitation hit on March 18 when attackers dropped helper.jsp webshells. Rapid7 MDR caught attacks on manufacturing companies by March 27. Public reporting came April 22. SAP patched April 24. CISA added it to KEV on April 29. By May 5, opportunistic actors were piggybacking on webshells already deployed by nation-state groups.
The attack is embarrassingly simple: POST a JSP webshell to /developmentserver/metadatauploader, then browse to your uploaded file and execute arbitrary commands. Visual Composer is installed in 50-70% of SAP Java systems—that's a massive attack surface sitting on the internet.
Threat Intelligence
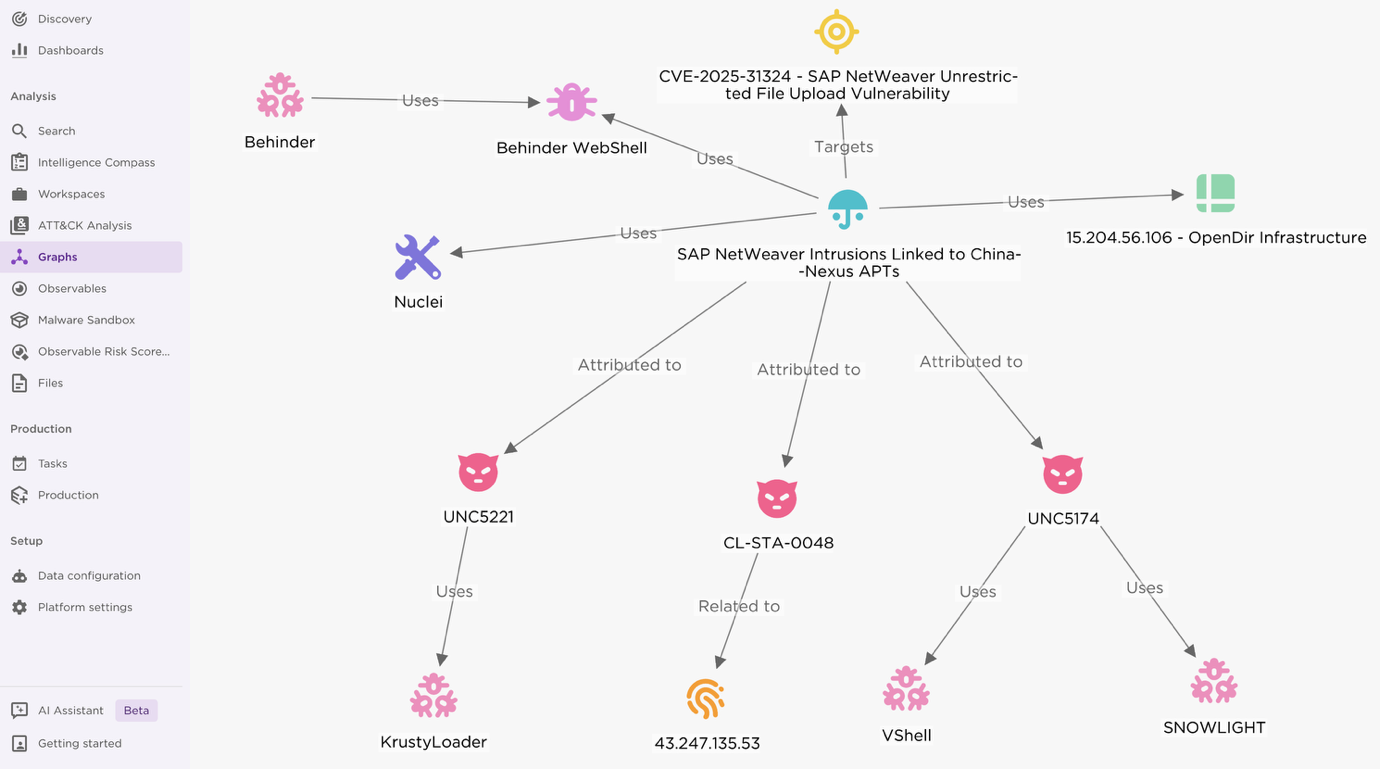
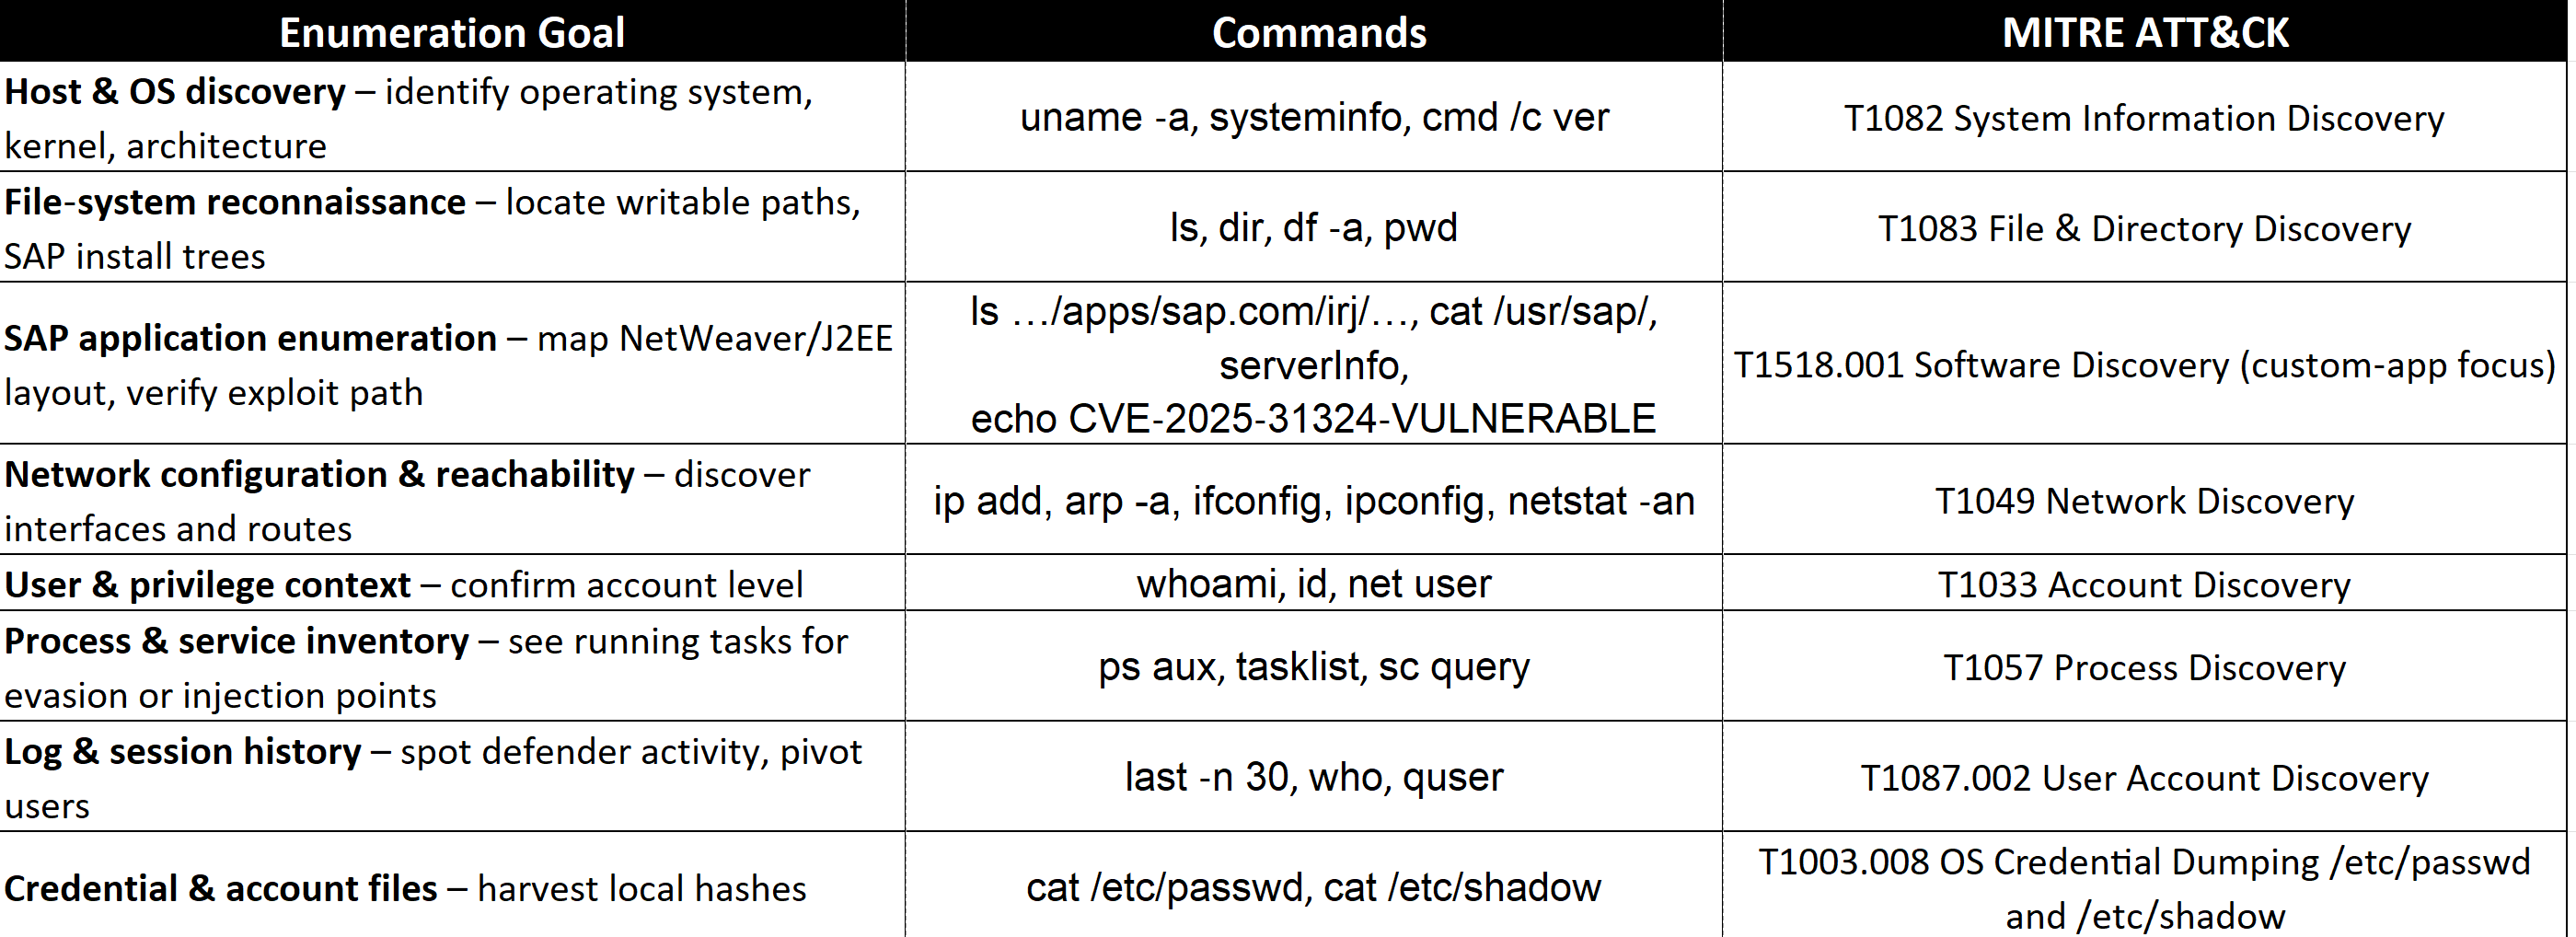
The attribution picture is crowded: UNC5221 (same group behind Ivanti attacks), UNC5174 (MSS affiliated), APT41/Winnti (confirmed by TeamT5), and Earth Lamia according to Trend Micro. Post-exploitation tooling includes VShell (Chinese C2 framework), SNOWLIGHT (custom backdoor with XOR encryption), KrustyLoader (Rust-based payload downloader), plus the usual Cobalt Strike and Brute Ratel beacons. This is serious nation-state capability aimed at critical infrastructure.
ERP systems like SAP are high-value targets for a reason: they contain financial records, HR data, supply chain information, and customer databases. They're typically connected to multiple internal systems with elevated privileges. And organizations are terrified to patch them because of uptime requirements—which means exploitation windows stay open for months.
IOCs for Threat Hunting
Look for webshells named helper.jsp, cache.jsp, or random 8-character strings like ssonkfrd.jsp in j2ee/cluster/apps/sap.com/irj/servletjsp/irj/root/. Check logs for POST requests to /developmentserver/metadatauploader. Known C2 IPs include 43.133.196.194 and 101.32.26.154. Also monitor for anomalous S3 bucket access—KrustyLoader stages payloads there.
Immediate actions: Apply SAP Security Note 3594142 today. Search for JSP files in your SAP servlet directories. Block access to /developmentserver/* endpoints at the firewall. If Visual Composer isn't business-critical, disable it entirely. Sources: Onapsis, EclecticIQ, Unit 42
May 2025: TeleMessage Breach — The Compliance Tool Became the Vulnerability
Here's a painful irony: U.S. government officials were using TeleMessage to archive their Signal and WhatsApp messages for regulatory compliance. The tool designed to keep them compliant got breached, exposing the exact communications they were trying to protect.
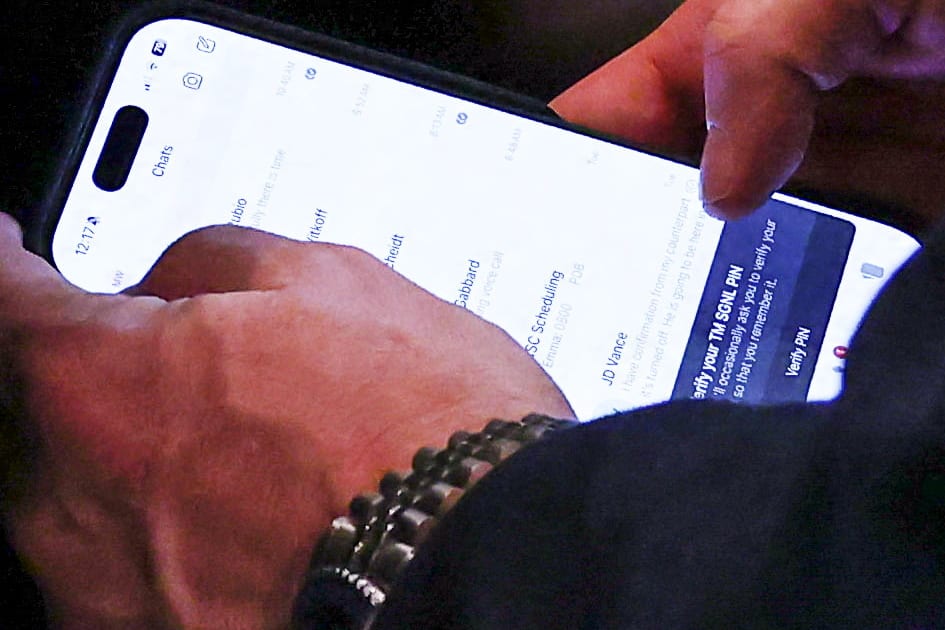
The exposed data included message archives, metadata (who talked to whom, when, how often), contact lists, and attachments. For intelligence services—foreign or domestic—this is gold. Communication patterns reveal relationships, timing reveals coordination, and attachments contain documents that were never meant to leave secure channels.
This is the compliance paradox in action: regulations require you to archive communications, which creates a centralized repository of sensitive data, which becomes a high-value target. You solve one risk by creating another.
Questions you should be asking: Where is your archived communication data stored? What security certifications does your archiving vendor hold? Do you have any visibility into their security posture beyond a SOC 2 report? What's your response plan if they get breached? Most organizations can't answer these questions—and that's a problem when you're trusting vendors with your most sensitive communications.
June 2025: Qilin Ransomware — 100 Victims in 30 Days
Qilin (also tracked as Agenda) has been operating since 2022, but June 2025 was their best month yet: 100 victims in 30 days, bringing their total to 800+ across 50+ countries. They're running a classic RaaS operation, and business is booming.
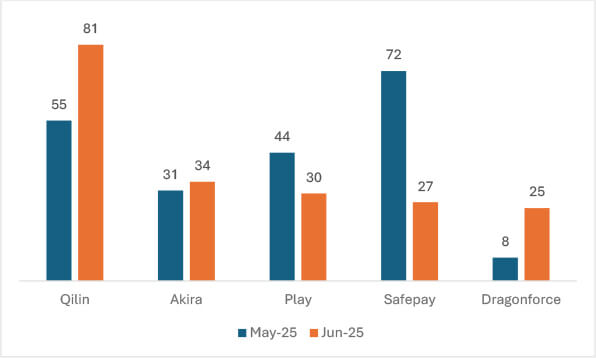
Their initial access playbook is what we see across most ransomware groups: stolen VPN credentials purchased from dark web marketplaces, exploitation of FortiGate vulnerabilities (CVE-2024-21762, CVE-2024-55591), phishing for credential harvesting, and good old RDP brute force against internet-exposed systems. Nothing exotic—just consistent execution of proven tactics.
Once inside, it's the standard kill chain: map AD, dump LSASS for credentials, lateral movement via RDP/PsExec/WMI, exfiltrate valuable data, then encrypt everything and hit victims with double extortion—pay for decryption AND to prevent data publication.
Healthcare and manufacturing took the worst hits. Hospitals had systems encrypted and patient data stolen. Manufacturing plants had production lines halted. Universities lost research data. Law firms had case files leaked. The sectors with the most sensitive data and the least tolerance for downtime are exactly what ransomware groups target.
What to do: Monitor dark web markets for your credentials—that's where initial access often starts. Patch your FortiGate appliances. Kill exposed RDP. Segment your network so lateral movement becomes harder. These aren't new recommendations, but clearly not enough organizations are following them.
July 2025: Change Healthcare — 192.7 Million Records, The Full Picture
It took over a year, but in July 2025 we finally got the full number: 192.7 million patient records stolen in the February 2024 Change Healthcare breach. That's 58% of the U.S. population. The largest healthcare data breach in history, and it happened because MFA wasn't enforced on an external-facing system.
ALPHV/BlackCat hit Change Healthcare in February 2024. UnitedHealth paid a $22 million ransom. Healthcare payment processing was disrupted nationwide for months—providers couldn't get paid, patients couldn't get medications authorized. The total cost to UnitedHealth: $2.87 billion and counting.
The exposed data is everything: PHI (medical records, diagnoses, treatments), PII (SSNs, addresses, birthdates), financial data (insurance information, billing), and payment data (bank accounts for healthcare providers). This data will be exploited for identity theft, insurance fraud, and targeted attacks for years.
Here's what makes this a systemic event: Change Healthcare processes 15 billion healthcare transactions annually—roughly 50% of all U.S. healthcare claims. One company, one attack, half the country's healthcare payment infrastructure offline. That's not a vendor dependency; that's a single point of failure for critical infrastructure.
The lesson that should have been obvious: MFA on external-facing systems isn't optional. UnitedHealth's congressional testimony confirmed that attackers got in via compromised credentials on a system without MFA. One of the largest companies in the world, handling the most sensitive data imaginable, and they didn't enforce MFA. If you're in healthcare IT and you don't have MFA everywhere, you're the next headline.
August 2025: Jaguar Land Rover — When One Company Takes Down an Economy
The Cyber Monitoring Centre classified the JLR attack as a "systemic cyber event"—their term for when a single incident causes economy-wide damage. And they weren't exaggerating: £1.9 billion in total UK economic impact, 5,000+ suppliers affected, and a £2 billion government bailout to keep the automotive supply chain from collapsing.
The attack hit on August 31, 2025. Within days, JLR halted all production—UK plants at Solihull, Castle Bromwich, and Halewood went silent. The Slovakia plant stopped. Global facilities in Brazil, India, and China followed. Weekly losses ran £50M+, about 1,000 vehicles per day not being built.
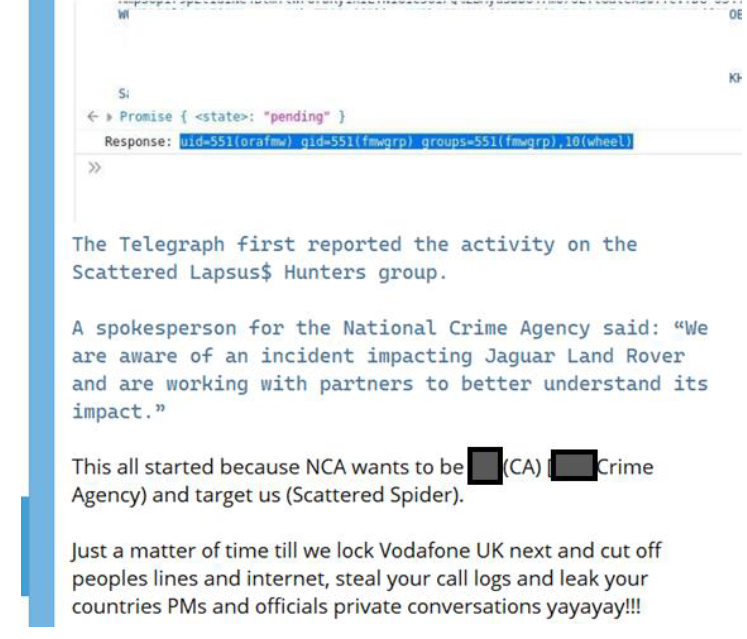
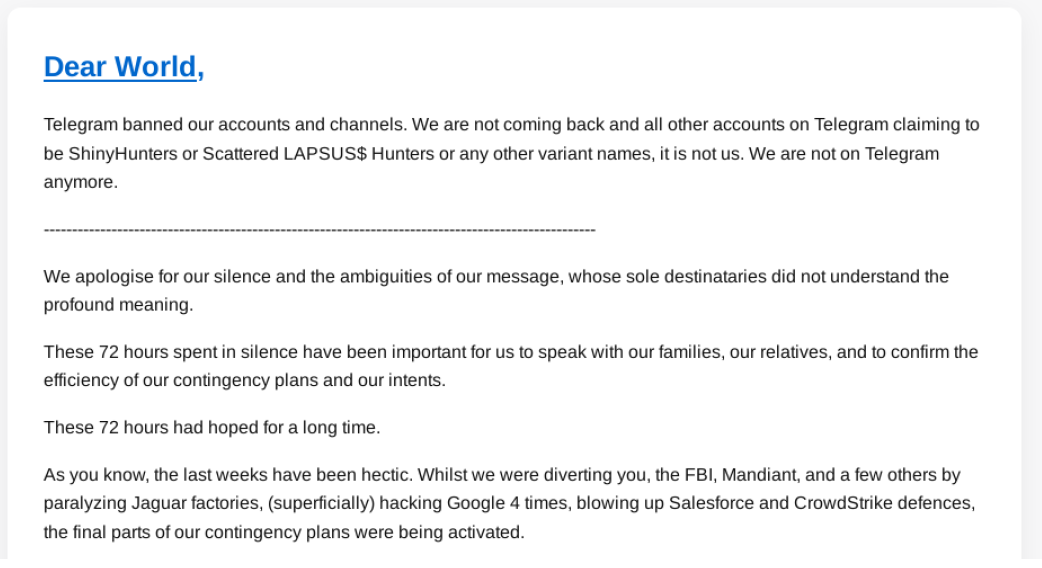
But here's what turned a major incident into a systemic event: the supply chain. JLR has 5,000+ direct suppliers in the UK—Tier 1 suppliers who make components, Tier 2 sub-suppliers, and Tier 3+ extended chain companies. When JLR stops ordering, they all stop producing. Steel, aluminum, electronics, interiors—entire industries went on pause. By mid-September, suppliers were furloughing workers. The UK government stepped in with a £2 billion emergency loan because the alternative was cascading bankruptcies across the automotive sector.
Impact Visualization
The attack vector hasn't been publicly disclosed—likely ransomware or a wiper targeting OT/IT interconnections. What we do know is that the blast radius extended far beyond JLR's network. This is what systemic risk looks like: one company's IT failure becomes the country's economic problem. (CM-Alliance)
Lessons for manufacturing: Your business continuity plans need to assume weeks of outage, not days. Your cyber insurance probably doesn't cover the full exposure. Your supply chain partners are your risk surface—if they can't produce because of your outage, you've just multiplied the damage. Air-gap your OT networks, map your critical suppliers, and understand that in modern manufacturing, a cyber incident isn't just your problem.
September 2025: European Airport Attacks — Coordinated Disruption
Heathrow, Brussels, Berlin Brandenburg—coordinated attacks hit major European airports in September, timed to maximize disruption during peak travel. The attackers went after IT infrastructure, not air traffic control, which tells you they understood exactly what would cause maximum chaos without triggering the most severe countermeasures.
Check-in systems went down at Heathrow. Baggage handling failed at Brussels. Display boards and comms were hit at Berlin. Thousands of passengers stranded, flights delayed across the continent. Attribution is still under investigation, but the coordination strongly suggests nation-state involvement—this wasn't opportunistic ransomware.
The attackers made a calculated choice: passenger-facing systems are interconnected with commercial IT networks and often poorly segmented from the internet. Air traffic control sits behind hardened barriers. Hit the soft targets, cause chaos, maintain plausible deniability because no planes fell out of the sky.
For critical infrastructure operators: Your commercial IT isn't as isolated as you think it is. Segment ruthlessly. Develop manual fallback procedures for every critical process—because when systems go down, your staff needs to keep operating. And understand that coordinated attacks against multiple facilities in your sector are now a realistic scenario, not a hypothetical.
October 2025: Oracle EBS Zero-Day — Clop Goes After ERPs
Clop keeps expanding their target list. After file transfer solutions, they turned to Oracle E-Business Suite (EBS) with CVE-2025-61882—a critical zero-day in enterprise financial systems that organizations literally cannot take offline without halting business operations.
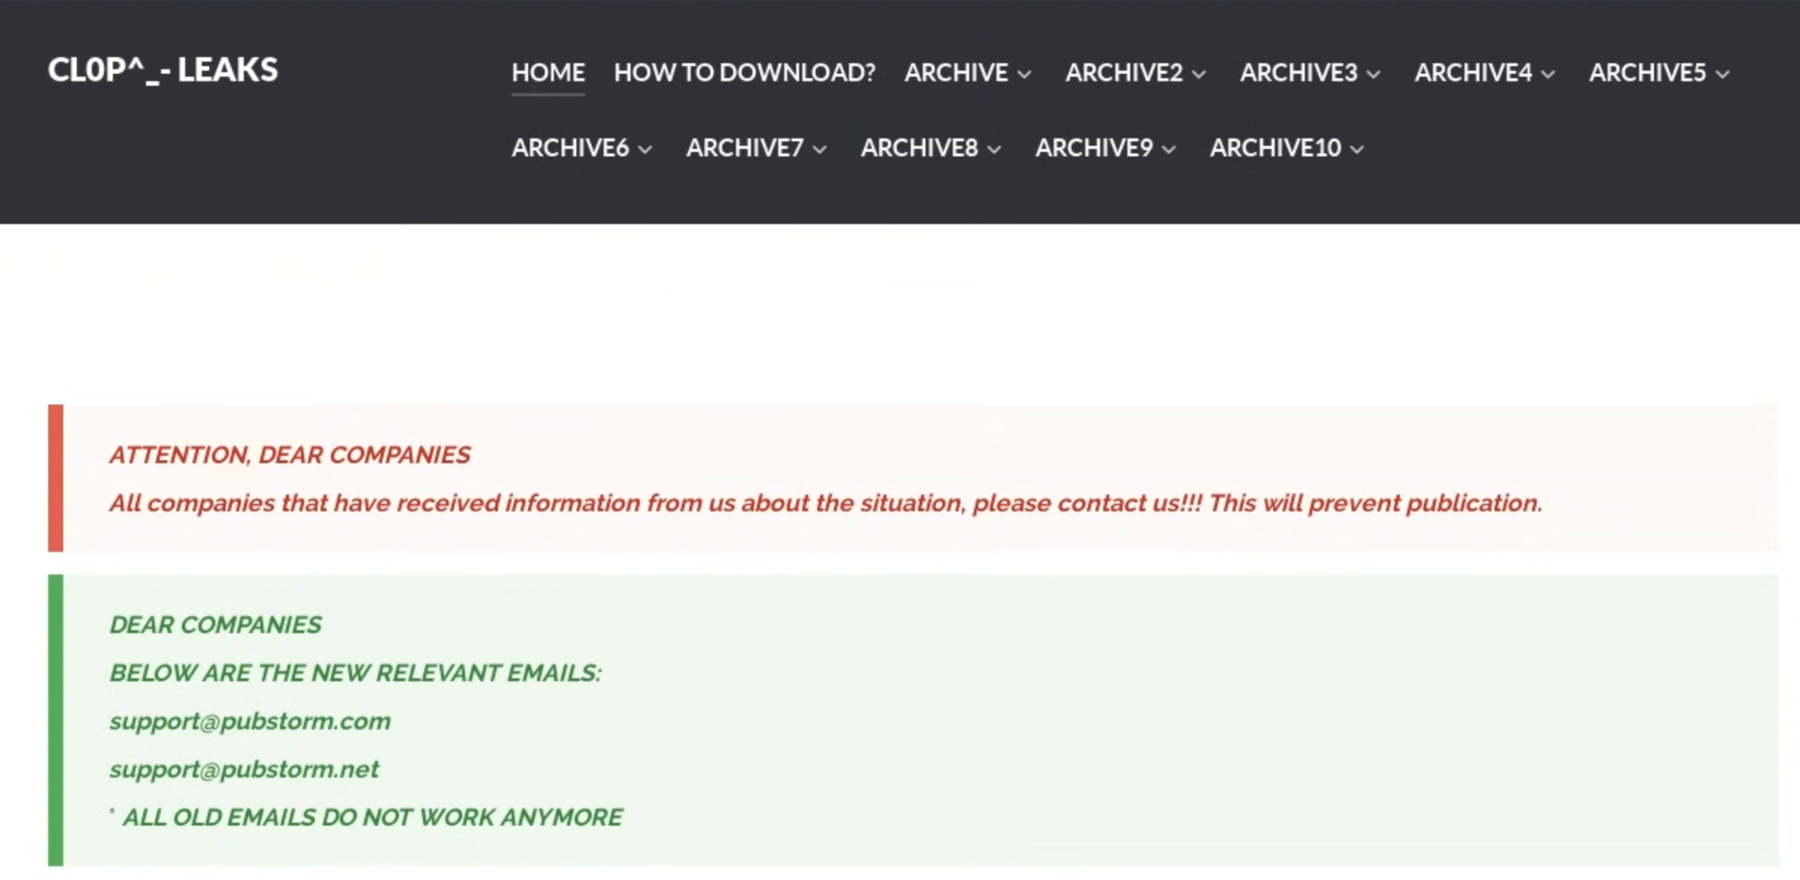
The attack pattern is identical to their Cleo campaign: find widely-deployed enterprise software, develop a zero-day, mass exploit before patches exist. Oracle EBS is running financial management at thousands of enterprises worldwide—general ledger, AP/AR, payroll, procurement. It's the backbone of business operations, which makes it the perfect extortion target.
Clop's evolution is worth tracking: MOVEit Transfer in 2023 (2,500+ victims), Cleo in February 2025 (335+ victims), now Oracle EBS. Each campaign targets software that's critical enough that organizations can't easily patch it and valuable enough that victims will pay to recover.
Immediate actions: Apply Oracle's Critical Patch Update. Restrict external access to EBS instances—they shouldn't be internet-facing. Deploy WAF rules to block exploitation patterns. And accept that Clop will find another target next quarter; proactive monitoring of security advisories for your critical infrastructure is now a survival requirement.
November 2025: Coupang — 5 Months of Undetected Compromise
South Korea's largest e-commerce company was breached for five months before anyone noticed. 33.7 million customer accounts exposed. The CEO resigned. That last part is significant—executive accountability for security failures is becoming real.
Five months is not unusual. It's actually the global average for dwell time—the period between initial compromise and detection. Five months gives attackers time to map your entire network, identify your most valuable data, establish persistence mechanisms in multiple locations, and potentially compromise your backups. By the time you detect them, they've already won.
The exposed data at Coupang included account credentials, personal information, purchase history, and partial payment card data. Standard e-commerce breach, standard impact: identity theft, account takeovers, and targeted phishing for years to come.
The CEO resignation matters: Security used to be an IT problem. When executives lose their jobs over breaches, it becomes a boardroom priority. Expect more organizations to invest in threat hunting, 24/7 EDR monitoring, and regular purple team exercises—not because they're best practices, but because executives are now personally exposed.
December 2025: React2Shell — From Disclosure to Mass Exploitation in Hours
CVE-2025-55182, "React2Shell," is a perfect 10.0 CVSS—remote code execution in React Server Components, affecting React 19+ and Next.js 13+ applications. Within hours of public disclosure, automated exploitation was happening globally. Not days. Hours.
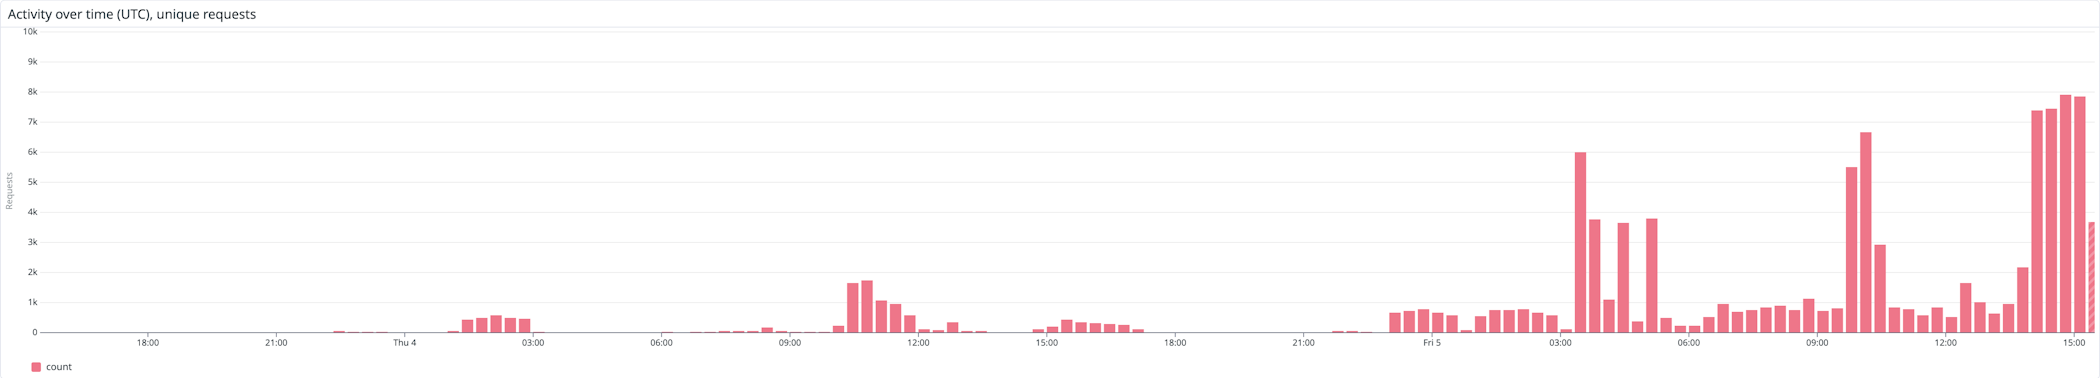
The vuln exists in how Server Components handle serialized data. Craft a malicious payload, send it to a vulnerable app, achieve arbitrary code execution on the server. The attack chain is fully automatable: scan for React/Next.js apps, fingerprint for Server Components, exploit, deploy webshells or cryptominers.
This is the new reality for disclosure-to-exploitation timelines. In 2020, you had weeks to months. By 2023, it was days. In 2025, it's hours. Manual patching processes can't keep up anymore. If you're not running automated dependency updates (Dependabot, Renovate), you're accepting that attackers will have a window to exploit every new CVE before you respond.
Actions: Update React and Next.js immediately. Deploy WAF rules to block exploitation patterns. Set up automated dependency monitoring for every framework in your stack. Datadog Security Labs published comprehensive IOCs: React2Shell IOCs on GitHub
2025 Ransomware Landscape
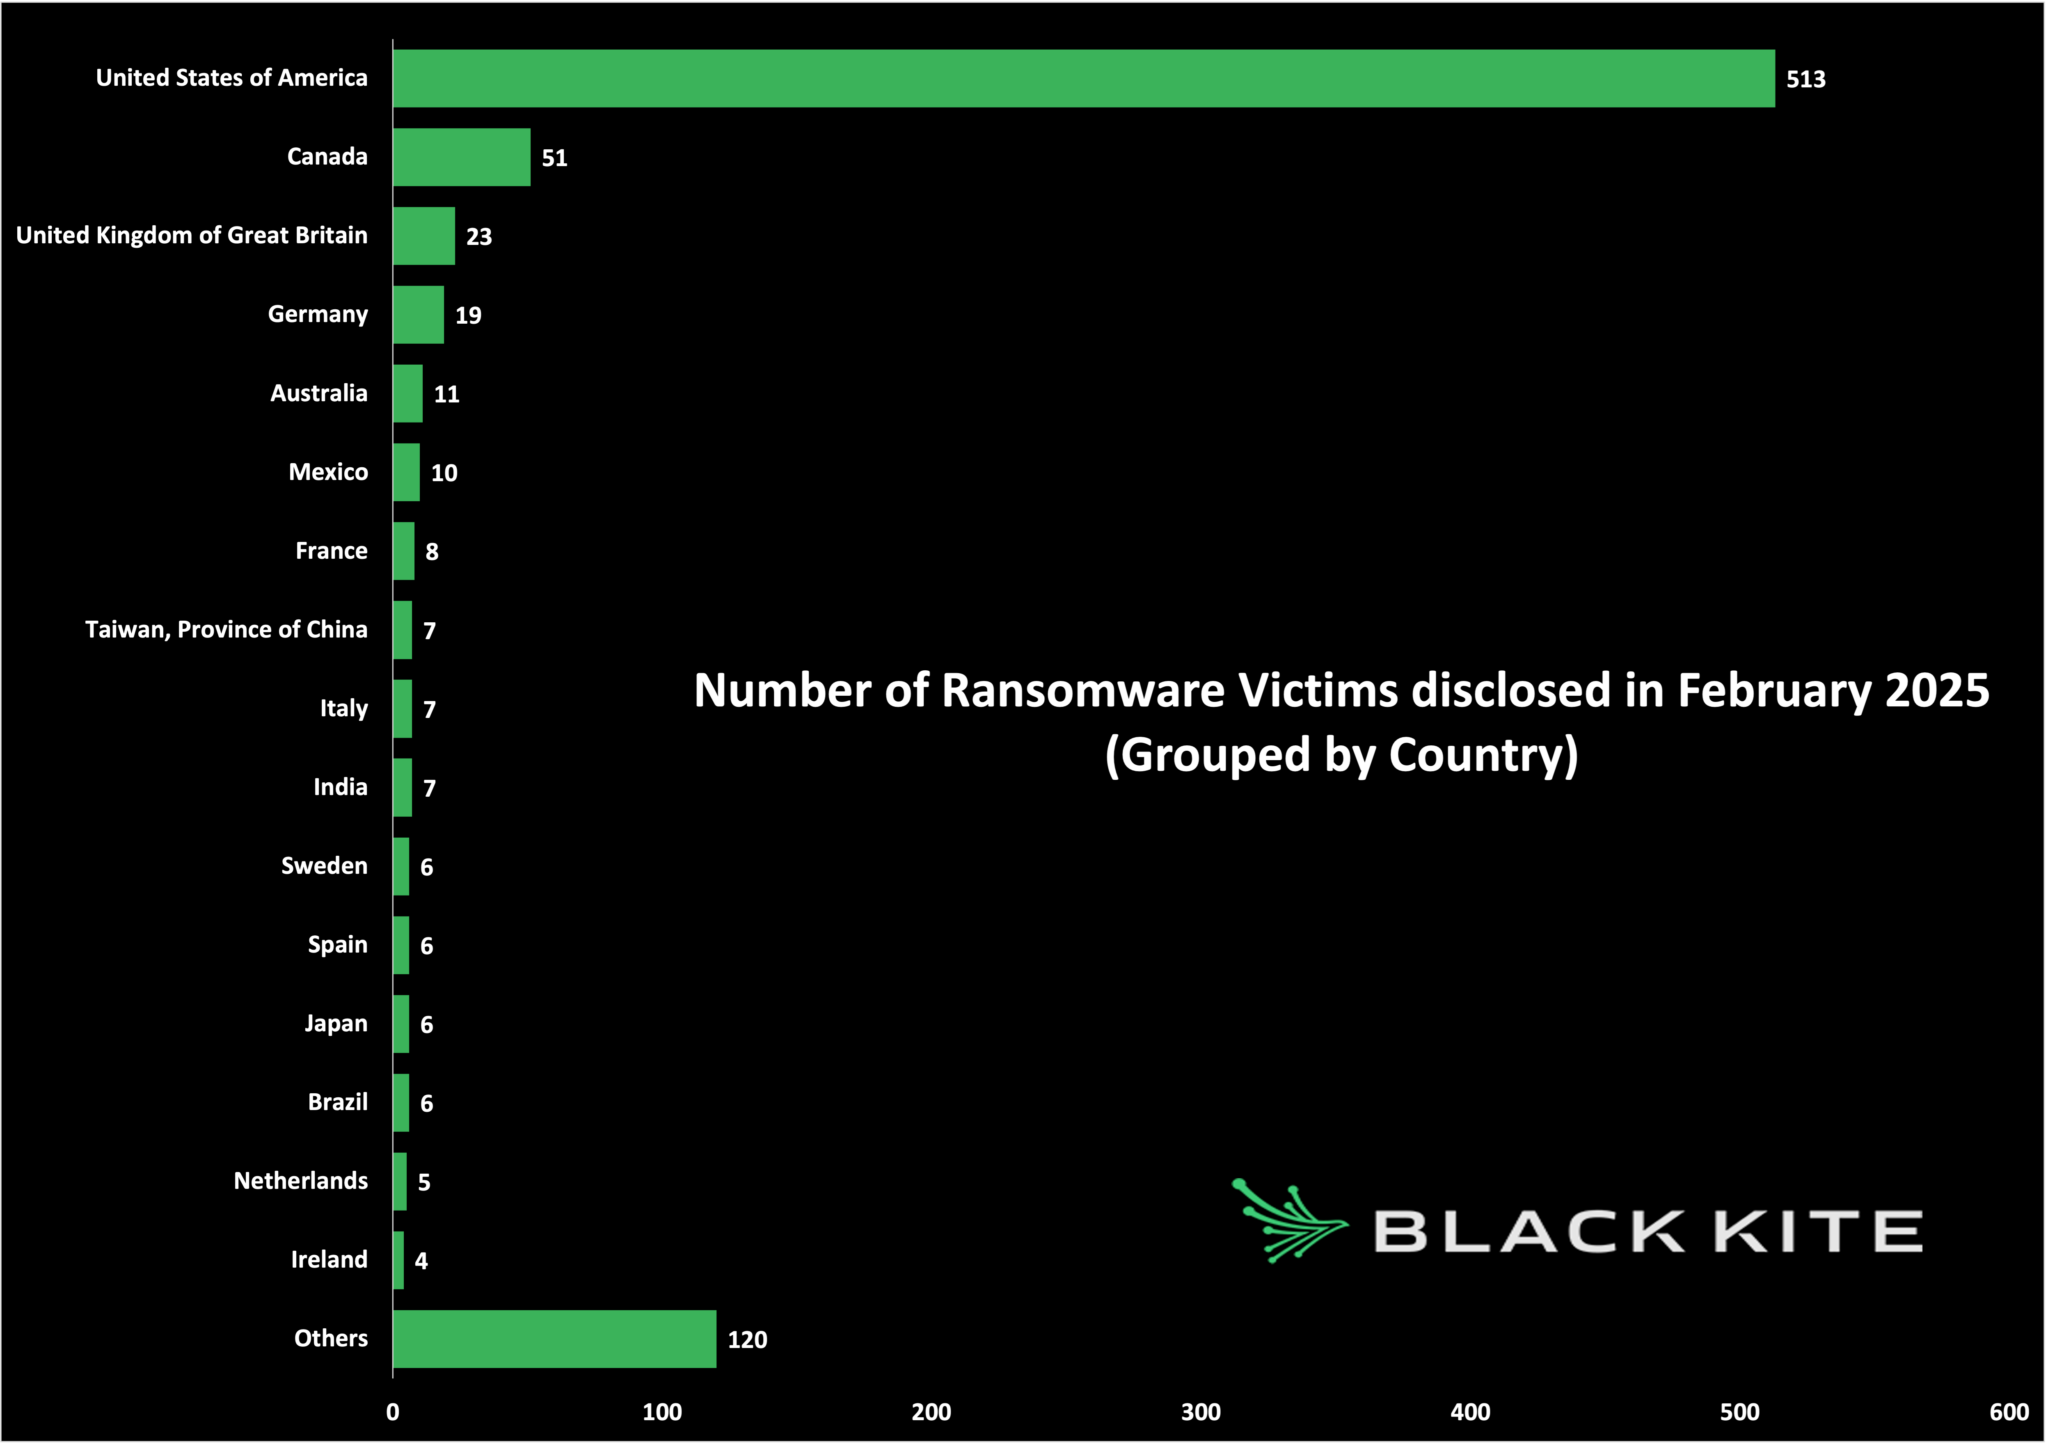
The numbers paint a clear picture: 4,701 ransomware incidents in the first nine months of 2025, a 34% increase year-over-year. Qilin hit 800+ victims across 50+ countries, peaking at 100 per month in June. Clop dropped 335 victims in February alone through the Cleo file transfer campaign.
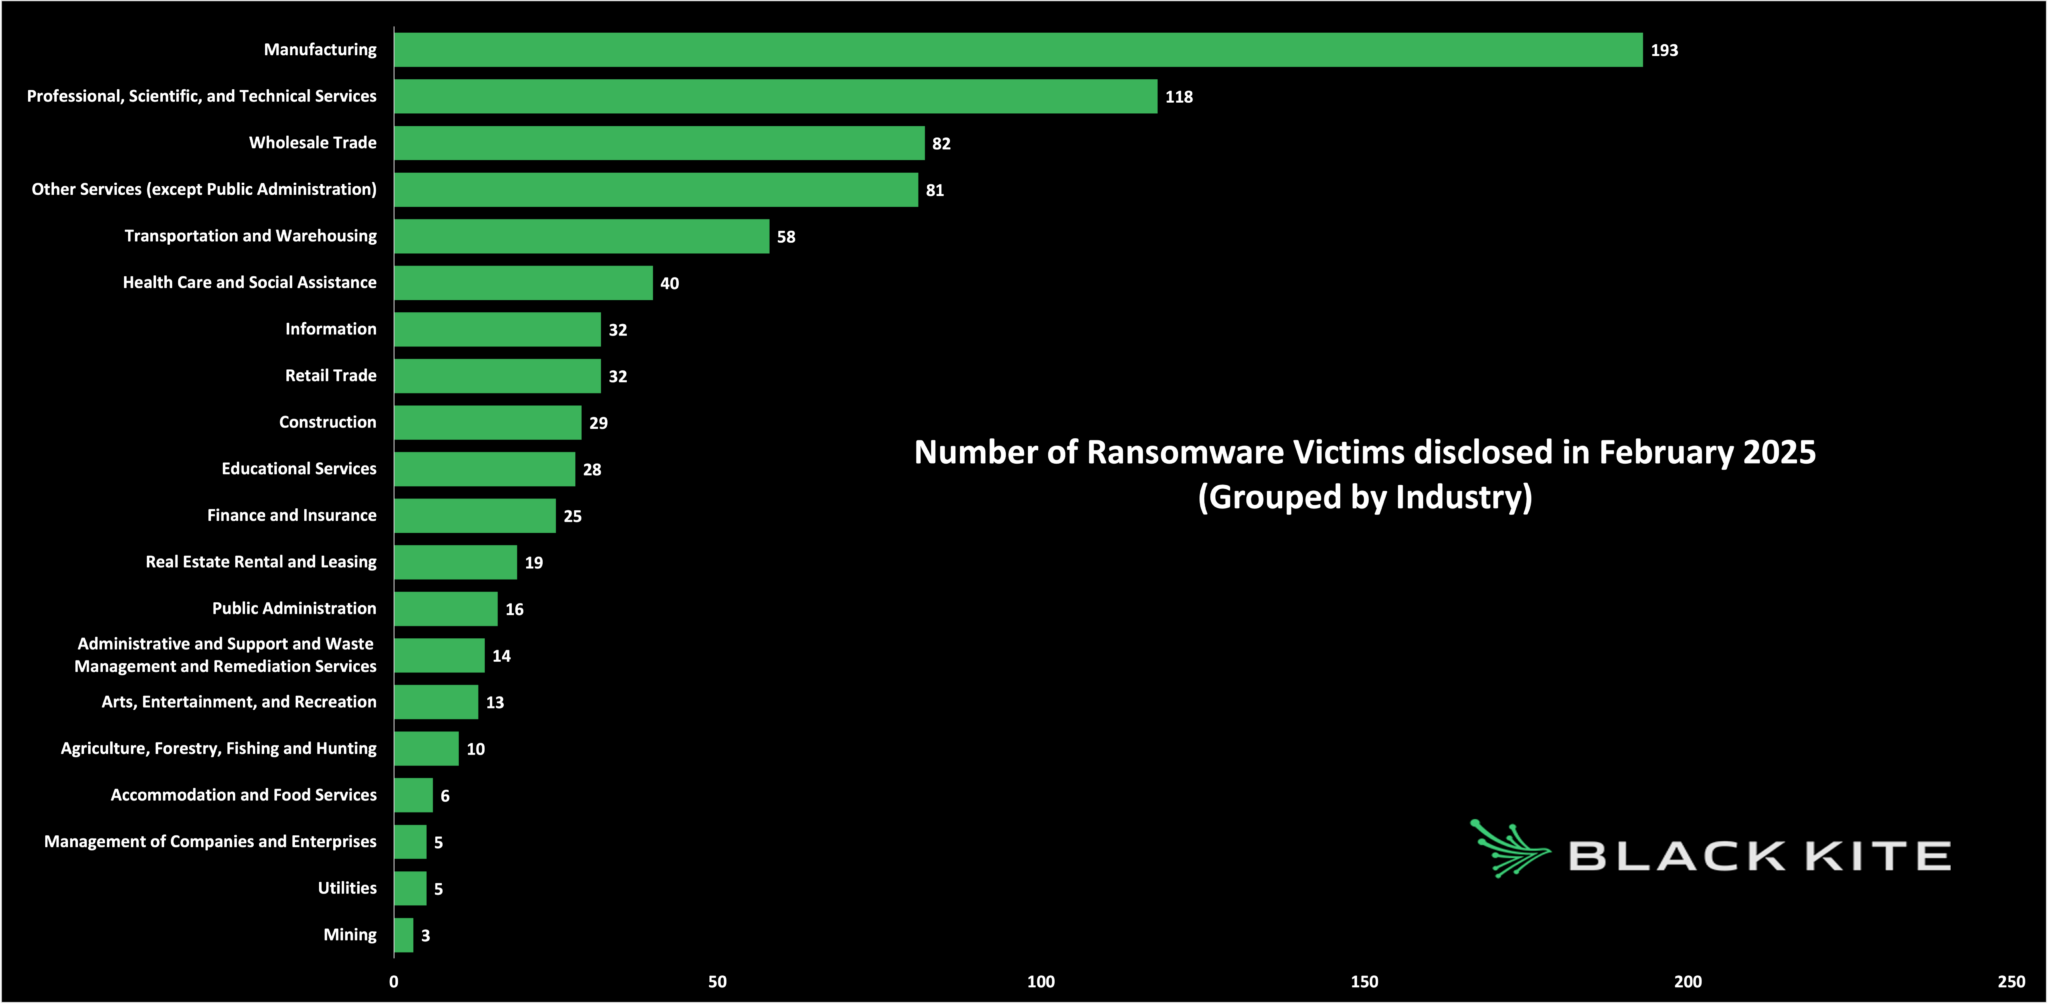
The initial access vectors are consistent across groups: leaked VPN credentials purchased from dark web markets, FortiGate vulnerabilities (CVE-2024-21762, CVE-2024-55591), SAP NetWeaver (CVE-2025-31324), and Veeam Backup (CVE-2023-27532). Nothing exotic—just relentless exploitation of the same attack surfaces.
File transfer solutions and edge devices remain primary targets because they're internet-facing, business-critical, and often poorly monitored. The defense is straightforward even if it's not easy: patch aggressively, monitor dark web markets for your credentials, and assume your perimeter devices are targets.
Critical Vulnerabilities of 2025
The highest-impact CVEs of the year share common characteristics: they hit edge devices and enterprise software, and exploitation started before or immediately after disclosure.
| CVE | Product | CVSS | Exploitation |
|---|---|---|---|
| CVE-2025-55182 | React/Next.js | 10.0 | Hours after disclosure (Datadog) |
| CVE-2025-31324 | SAP NetWeaver | 10.0 | 581+ instances compromised by APTs |
| CVE-2025-0282 | Ivanti Connect Secure | 9.0 | Exploited before disclosure |
| CVE-2024-55956 | Cleo File Transfer | Critical | 335+ victims in Clop campaign |
| CVE-2025-61882 | Oracle EBS | Critical | Ongoing Clop exploitation |
If you're running any of these products, assume you've already been scanned. The attackers certainly did.
AI-Powered Fraud — The Arup Deepfake Case
A finance employee at Arup Group joined a video call with the CFO and three senior managers. Over several days, they executed 15 wire transfers totaling $25.5 million. The problem: every single person on that call except the victim was AI-generated. (WEF)
This isn't science fiction anymore. Q1 2025 saw $200M+ in deepfake fraud losses. Voice phishing increased 442%. The barrier to creating convincing deepfakes has collapsed—consumer AI tools can now generate passable video in about 45 minutes per person. All attackers need is public footage of executives from webinars, company videos, or social media.
Attack Visualization
The defense is straightforward but requires culture change: Multi-channel verification for all large transactions. If "the CFO" calls requesting an urgent wire transfer, you call back on a known number. If executives want to skip verification protocols because it's "time-sensitive," that's exactly when you don't skip them. Video and voice are no longer reliable authentication factors.
Regulatory Landscape
2025 brought more compliance burden. New state privacy laws in Nebraska, New Hampshire, and New Jersey took effect in January—audit your applicability if you haven't already. The DOJ's Data Security Program (April 2025) adds controls for bulk data transfers, particularly relevant if you're moving sensitive data internationally. CIRCIA's 72-hour reporting requirement continues tightening incident response timelines—if your IR process takes longer than three days to assess reportability, you're not compliant.
Five Hard Lessons from 2025
1. Help desks are attack surfaces. M&S, Co-op, and Harrods lost £500M+ because someone called the help desk and asked for a password reset. Out-of-band verification—calling back to a registered number—would have stopped it.
2. Your vendors' security is your security. Bybit got owned because a Safe{Wallet} developer ran the wrong Docker project. Change Healthcare exposed 192.7M records because they didn't enforce MFA. You can't outsource accountability.
3. Hardening isn't optional. React2Shell and Cleo both exploited default configurations. If you're deploying enterprise software with defaults, you're deploying vulnerabilities.
4. Detection matters more than prevention. Coupang was breached for 5 months before anyone noticed. If you're not actively threat hunting, you won't find attackers until they announce themselves.
5. Manual patching is a losing game. When exploitation starts hours after disclosure, your patch-on-Tuesday-deploy-next-week process is already too slow. Automated patching isn't just convenient—it's necessary for survival.
What to Do About It
This week: Verify your help desk has identity verification procedures that can't be bypassed by a convincing phone call. Confirm your offline backups exist and are actually offline. Check patch levels on VPN appliances, firewalls, and file transfer systems—those are the first things that get scanned.
This month: Run a vendor security assessment on your top 10 critical suppliers—ask the hard questions about MFA, incident response, and recent security audits. Conduct an IR tabletop with a ransomware scenario that includes supply chain impact. Audit your AD configuration for NTDS.dit protection, tiered admin accounts, and Credential Guard.
This quarter: Train your finance team on deepfake recognition and establish callback verification protocols for large transactions. Review your cyber insurance coverage against actual exposure—most policies have exclusions and sublimits that don't match real-world incidents. Set up regular board reporting on cybersecurity metrics and incidents.
Appendix: IOCs
Clop Campaign IPs
185.181.230.103, 181.214.147.164, 176.123.5.126, 5.149.249.226
209.127.12.38, 192.119.99.42, 176.123.10.115, 185.162.128.133
IOC Repositories
| Threat | Resource |
|---|---|
| React2Shell | Datadog GitHub |
| Qilin | Cisco Talos GitHub |


