
INC Ransom Lists Adiance Technologies as a Breach Victim
The ransomware group INC Ransom has named Adiance Technologies as a victim, claiming to have stolen data from the company and publishing an entry on its leak site. Adiance is an Indian manufacturer of surveillance cameras and video systems.
The listing indicates the organisation was compromised and that data was exfiltrated. Based on the material the group has posted, the stolen set may include research and development documents alongside commercial and financial records.
About INC Ransom
INC Ransom is a double-extortion group that has been active since 2023. Its method combines two forms of pressure: it steals data before encrypting systems, then runs a leak site where victims are named and files are released in stages until a payment is made.
A public listing usually means the group has moved past private negotiation and is using the stolen data as leverage. The group has claimed victims across several sectors and regions, and its leak site carries entries for many organisations unrelated to this one.
The Company
Adiance is an NDAA-compliant OEM and ODM manufacturer that sells under the ArcisAI brand. It builds cameras and video software that other companies rebrand and deploy, which places it upstream of a range of resellers and their customers.
This position is what gives the breach weight. A manufacturer's designs, firmware, and software sit behind many downstream products. When the maker is compromised, the concern extends beyond a single company to the products and deployments built on its technology.
What May Be Exposed
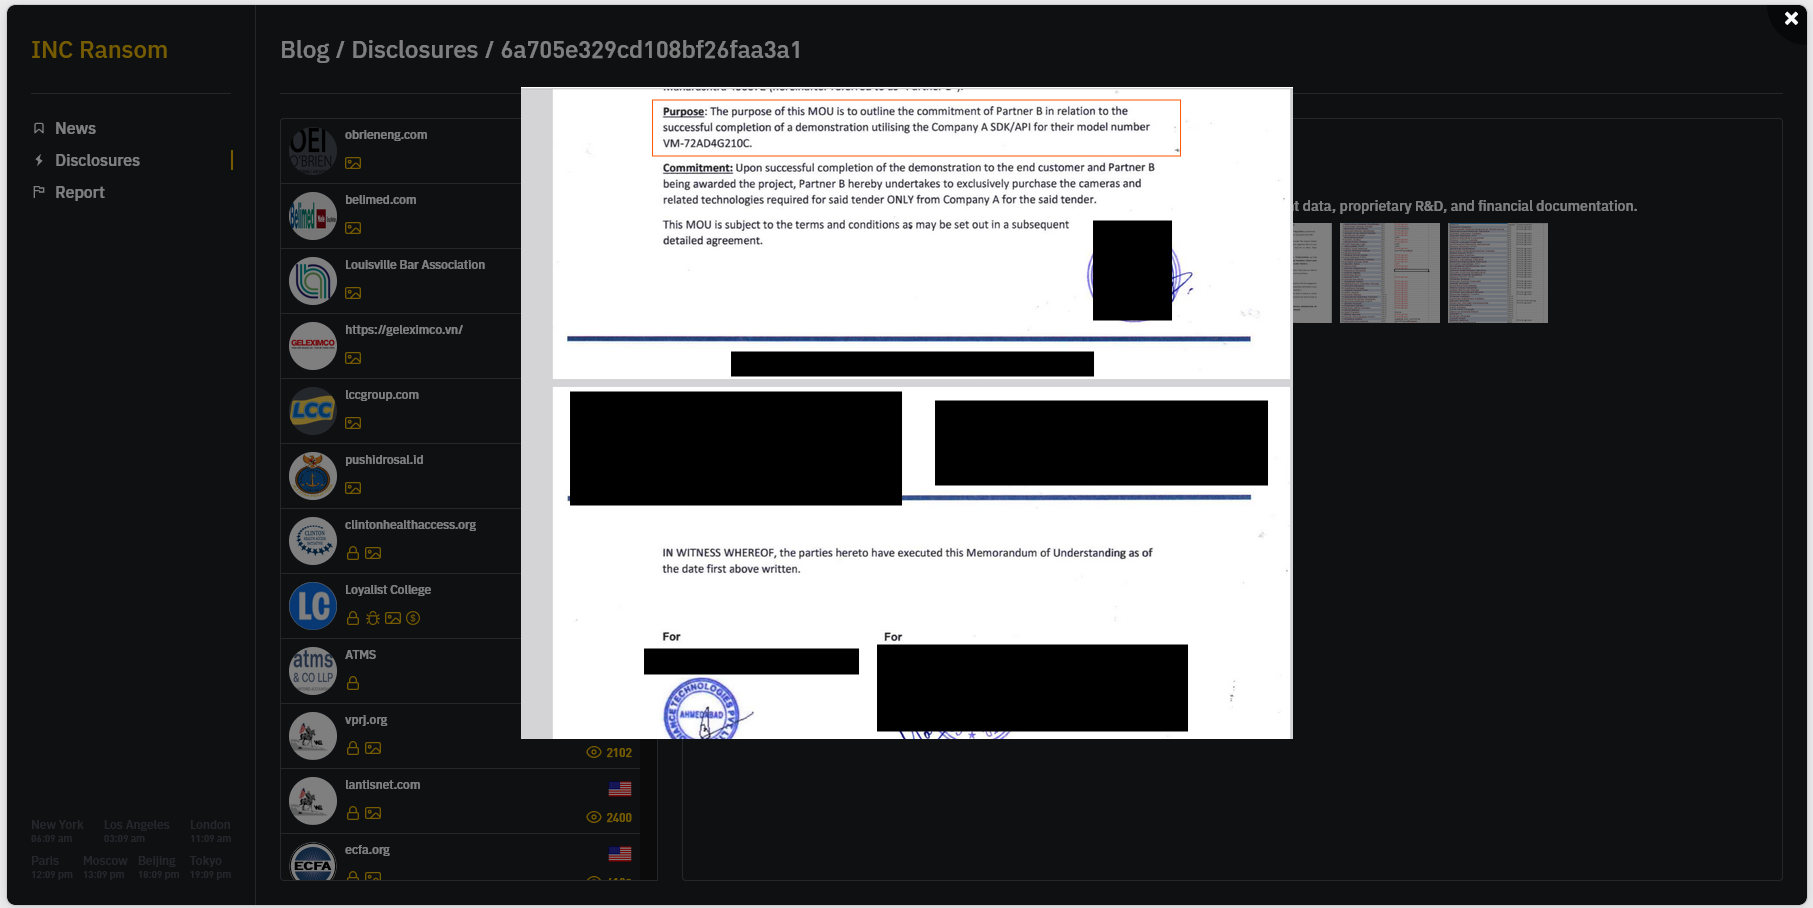
INC Ransom claims the stolen archive holds contract data, financial records, and proprietary research and development. The sample it has posted references Adiance's SDK and API, which suggests product and software development material may be part of the breach.
For a hardware manufacturer, research and development is core intellectual property. It can cover source code, firmware, design documents, and the interfaces that partners integrate against. Exposure of that material can reveal how products work internally and affect a company's competitive position. The full contents of the archive are not confirmed, and the descriptions are the group's own.
Why It Matters
Surveillance equipment makers are attractive targets because their products are deployed widely and often operate in sensitive environments. A breach at the manufacturer level raises questions that a single end-user breach does not, about the integrity of the technology and the confidentiality of what the manufacturer holds on its partners and deployments.


