
Executive Summary
On April 7, 2026, six U.S. federal agencies jointly warned that Iranian-affiliated actors are actively exploiting internet-facing Rockwell Automation PLCs across U.S. water, energy, and government infrastructure. The threat is real — and the story is significantly bigger than what is being reported.
- 8 attacker IPs extracted from the CISA STIX file — 2 have port 44818 open, 1 tagged "ics" in passive scan databases
- C2 infrastructure mapped via certificate transparency: 18+ nodes across Nigeria, Singapore, Albania, Germany — MQTT brokers deployed exactly 4 days before the first confirmed attack
- FBI seized the primary C2 domain (tylarion867mino.com → ns: fbi.seized.gov)
- Kupferle Water Solutions (Fenton, MO) — first named 2026 U.S. water target with HMI screenshot evidence from "APT IRAN"
- 27 Rockwell Automation employees with stolen ADFS/SSO credentials on the dark web right now
- Demonstrated capability to manipulate industrial processes — water pressure, chemical dosing, fuel systems — with access confirmed across multiple sectors
MITRE ATT&CK for ICS
By the Numbers
What Happened
On April 7, 2026, CISA published advisory AA26-097A, co-signed by CISA, FBI, NSA, EPA, DOE, and U.S. Cyber Command. The advisory states that "since at least March 2026," Iranian-affiliated actors have disrupted programmable logic controllers across U.S. critical infrastructure — specifically targeting water treatment, energy, and government facilities.
The targeted devices are Rockwell Automation CompactLogix and Micro850 PLCs — the same vendor whose equipment runs a significant portion of U.S. industrial control systems. According to the advisory, attackers used Studio 5000 Logix Designer (Rockwell's legitimate engineering software) and deployed Dropbear SSH on compromised controllers for persistent access.
The advisory lists five targeted ports:
2222 — Listed in advisory as targeted PLC port
502 — Modbus
102 — S7comm
22 — SSH (Dropbear deployment for persistence)
Every verifiable claim in the advisory was tested against primary sources. Some confirmed. Some did not.
| Claim | Verification |
|---|---|
| Internet-facing PLCs are being scanned | ICS port telemetry shows port 44818 scanning up 33% in April, peaking at 4,857 records on April 7 |
| Target shifted from Unitronics to Rockwell | Port 20256 (Unitronics) is flat in 2026 while port 44818 (Rockwell) is rising — confirmed in 4 years of sensor telemetry |
| IOCONTROL malware exists | SHA256 verified in malware databases, fully reverse-engineered with published technical analysis |
| CyberAv3ngers is IRGC-CEC affiliated | U.S. Treasury sanctioned 6 named IRGC-CEC officials; $10M bounty posted |
| C2 infrastructure was seized | WHOIS for tylarion867mino.com shows NS: ns1.fbi.seized.gov |
| Attackers used overseas-based IPs | STIX file contains 8 IPs — 7 in same /24 block, leased U.S. infrastructure |
The Evidence
Beyond the advisory itself — what the raw data from network sensors, certificate transparency logs, passive scanning databases, WHOIS records, and dark web intelligence actually shows.
CISA STIX IOCs — The Attacker IPs
The advisory's STIX IOC file (initially returning HTTP 403) contains 8 IP addresses attributed to the attackers.
| IP Address | Open Ports | Network | Notable |
|---|---|---|---|
185.82.73.162 |
135, 137 | WSOL /24 | Windows services |
185.82.73.164 |
1801 | WSOL /24 | MS Message Queuing |
185.82.73.165 |
80 (IIS 10.0) | WSOL /24 | Windows web server + ASP.NET |
185.82.73.167 |
44818 | WSOL /24 | tagged "ics" in passive scan data — EtherNet/IP |
185.82.73.168 |
No data | WSOL /24 | Dark / no response |
185.82.73.170 |
44818, 1801 | WSOL /24 | EtherNet/IP + MS Message Queuing |
185.82.73.171 |
135, 1801 | WSOL /24 | MS Message Queuing |
135.136.1.133 |
135 | NCR (different) | Separate network |
Source: CISA STIX file (AA26-097A), verified against passive scanning databases
Background — The Playbook They Used Before
The same group ran a confirmed campaign in November 2023 targeting Israeli-made Unitronics PLCs. That operation is relevant because it establishes the pattern now repeating at scale against American-made Rockwell systems.
The 2023 C2 infrastructure is now dead. Whatever the 2026 actors are using is new — and has not been disclosed. The CISA advisory provides attacker IPs from leased infrastructure but no C2 domains, no malware samples, and no infrastructure map for the current campaign.
ICS Port Scanning Telemetry — 2026 Campaign Window
Global sensor network data for the critical Rockwell port (44818/EtherNet-IP) shows a clear inflection in March-April 2026, reversing a months-long decline.
Port 44818 (Rockwell EtherNet/IP):
| Period | Avg Records/Day | Trend |
|---|---|---|
| Oct 2025 – Jan 2026 | 2,831 | Declining baseline |
| Feb 2026 | 2,640 | Below baseline |
| Mar 2026 | 3,010 | Reversing (+14%) |
| Apr 1-7, 2026 | 3,775 | Clear escalation (+33%) |
| Apr 7, 2026 | 4,857 | Single-day peak (+72%) |
Port 2222 (advisory-listed PLC port):
A significant anomaly appeared days before the U.S. strikes on Iran:
Feb 22: 1,281,915 — spike begins
Feb 23: 1,780,474
Feb 24: 2,350,914 — PEAK (4x baseline) — 4 days before strikes
Feb 28: 654,242 — drops on strike day
Apr 3-7: ~1,100,000 — secondary spike around advisory date
Port 20256 (Unitronics) — Target Shift Confirmed: Flat at ~2,700/day through February–April 2026. No increase. The focus has moved from Israeli-made to American-made PLCs.
Kupferle Water Solutions — The First Named 2026 Target
CISA named zero victims. Dark web monitoring captured something the advisory did not disclose.
On March 20, 2026, a Telegram post by "APT IRAN" included a screenshot showing access to a Kupferle 9800i-120-A-X-A water treatment controller. The screenshot reveals:
- Device date/time: 03/10/26 09:48:41 (March 10, 2026)
- Free Chlorine: 0000.00 PPM
- Temperature: 67.89 F
- Status: "Flushing in Progress"
- BV and SV values showing X (error/offline state)
- Persian text claiming access in Fenton, Missouri
- Claims of value manipulation and persistent access
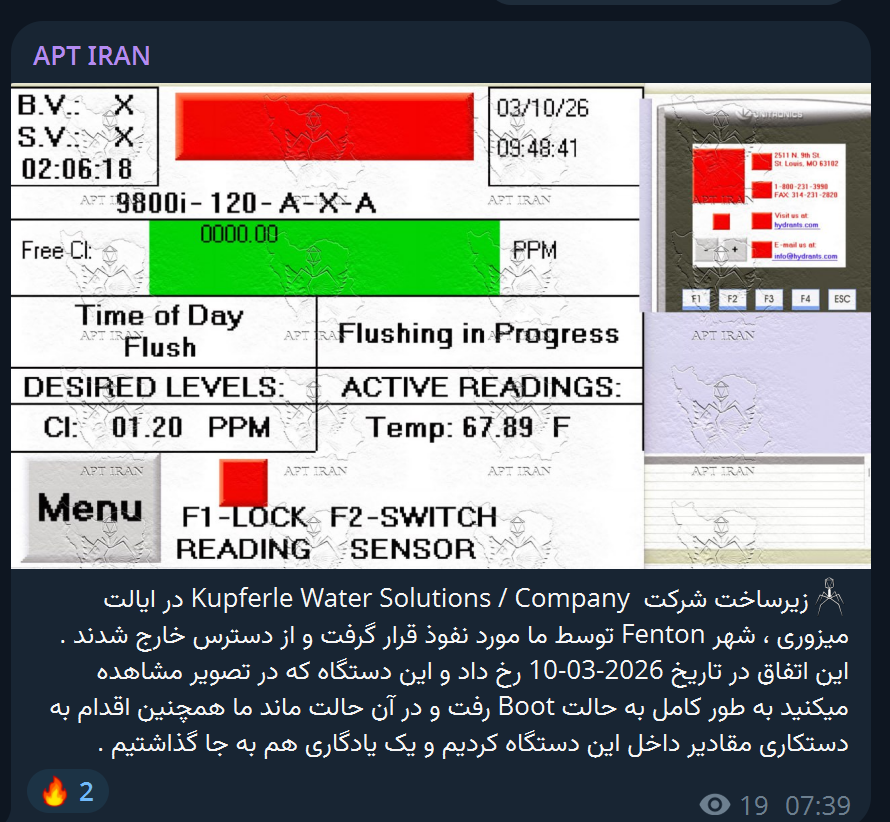
Kupferle is a real company — a water infrastructure equipment manufacturer based in St. Louis, Missouri, founded in 1897. They manufacture water main flushing systems, hydrants, and related equipment used by municipalities across the United States.
The Attack Nobody Is Reporting — Rockwell's Supply Chain
The most significant finding is not about PLCs. It is about Rockwell Automation's own corporate systems.
Dark web stealer log databases show 27 unique Rockwell Automation employees with credentials stolen by info-stealing malware and available on dark web markets, concentrated in March-April 2026.
| Internal System | Credential Count | Function |
|---|---|---|
fs.rockwellautomation.com/adfs/ls/ |
71 | ADFS Single Sign-On — gateway to all internal systems |
login.rockwellautomation.com |
31 | Main corporate login |
idp.rockwellautomation.com/adfs/oauth2/ |
21 | OAuth identity provider — API/app authentication |
mfaportal.rockwellautomation.com |
6 | Multi-factor authentication management |
iiq.rockwellautomation.com |
6 | Identity governance platform |
amt-ise01-redirect.ise.ra.rockwell.com |
4 | Cisco ISE — network access control |
Malware found on employee machines:
C:\Windows\System32\svchost.exe — masquerading as system process
C:\Windows\SysWOW64\explorer.exe — masquerading as Windows Explorer
Multiple IXP*.TMP\*.exe — staged payloads
Kiddion's Modest Menu.exe — game cheat (common malware vector)
Licence_Version_Loader.exe — pirated software (common malware vector)
23 unique IPs from compromised machines span Mexico, Taiwan, Japan, UK, Colombia, India, South Africa, and other countries — suggesting infections across Rockwell's global workforce.
Not SCADA — The Real Attack Surface
A critical misconception in public reporting: nearly every news outlet describes these as "SCADA attacks." They are not.
The primary targets are PLCs (Layer 1 controllers), not SCADA systems (Layer 2 supervisory). Attackers connect directly to PLCs via EtherNet/IP or PCOM protocols, bypassing SCADA entirely. SCADA displays are affected as a secondary consequence — they show whatever the compromised PLC tells them.
The 5 actual attack surfaces in this campaign:
- Internet-exposed PLCs — directly accessible via EtherNet/IP (port 44818)
- Default credentials — Unitronics Vision "1111", Rockwell factory defaults
- Legitimate engineering software — Studio 5000 used from leased infrastructure to create accepted PLC connections
- SSH persistence — Dropbear SSH deployed on compromised controllers (port 22)
- Supply chain — Rockwell employee credentials providing potential access to deployment data and firmware systems
Operational Impact
Across every confirmed incident, these actors have demonstrated the ability to reach and manipulate systems that control physical processes.
| Incident | Impact | Evidence |
|---|---|---|
| Aliquippa Water (Nov 2023) | Water pressure booster station taken offline. Facility switched to manual operations for ~7,000 residents. | Victim confirmed |
| Orpak/Gasboy Fuel Systems (2024) | IOCONTROL malware deployed on payment terminals with capability to shut down fuel pumps and exfiltrate card data. | Malware forensically confirmed |
| 2026 Rockwell Campaign | "Operational disruption and financial loss" across water, energy, and government sectors. PLC logic modified, HMI/SCADA data manipulated. | CISA + 6 agencies confirmed |
| Kupferle Water, MO (Mar 2026) | HMI access to water flushing controller. Claimed manipulation of device values and persistent access. | Screenshot evidence |
The Broader Threat Landscape
CyberAv3ngers is not operating in isolation. Dark web monitoring captured 50+ SCADA/water infrastructure attack claims in just three months (February–April 2026) across multiple groups:
| Actor | Targets | Attribution |
|---|---|---|
| Z-PENTEST ALLIANCE | Israel water pumps, S. Korea water treatment, Italy heating systems | Pro-Russian |
| NoName057(16) | Israel pumps, Spain SCADA, Sweden water, Poland wastewater | Pro-Russian |
| Infrastructure Destruction Squad | India water, S. Korea, US + Australia water distribution | Anti-infrastructure |
| OverFlame | Ukraine food facility SCADA, Ukraine infrastructure | Pro-Russian |
| APT IRAN | Kupferle Water Solutions (USA), Lockheed Martin (claimed) | Iranian state |
| CyberAv3ngers | U.S. ICS (water + energy) | IRGC-CEC |
| Handala | Stryker (USA), threatens all water/electricity/oil | MOIS |
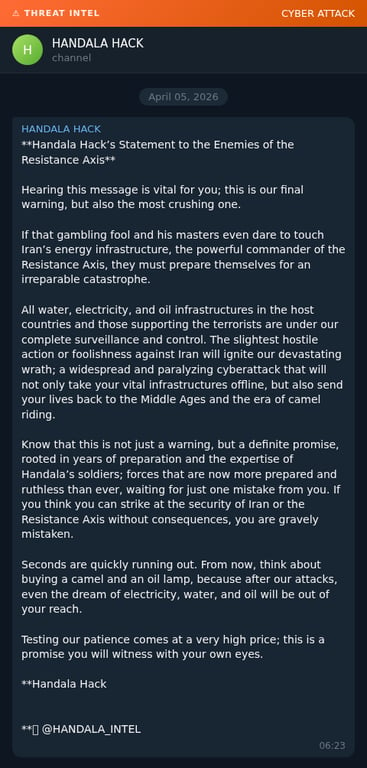
ICS/SCADA targeting is not an Iranian monopoly — it is a global trend with multiple state and non-state actors converging on the same attack surface: internet-exposed industrial controllers with weak or default credentials. The Stryker attack (Handala/MOIS) is a completely different organization from CyberAv3ngers (IRGC-CEC) — different sponsor, different methods, different targets.
2026 Campaign Timeline
Chronology of the current campaign, reconstructed from dark web intelligence, ICS port telemetry, and government disclosures.
MITRE ATT&CK for ICS — Full Mapping
| Technique ID | Name | Application in This Campaign |
|---|---|---|
| T0883 | Internet Accessible Device | 40,000+ U.S. ICS devices directly exposed to the internet, including Rockwell CompactLogix and Unitronics Vision PLCs |
| T0886 | Remote Services | Attackers use Studio 5000 from leased infrastructure to create accepted EtherNet/IP connections to victim PLCs |
| T0855 | Unauthorized Command Message | PLC logic modified to alter controller behavior. Dropbear SSH deployed for persistent access on port 22 |
| T0831 | Manipulation of Control | Kupferle screenshot shows "Flushing in Progress" with manipulated values. Aliquippa HMI defaced with anti-Israel messaging |
| T0829 | Loss of View | Operators see fake readings while PLCs run attacker-modified logic. The screen shows normal; the reality is compromised |
| T1078 | Valid Accounts — Default Credentials | Unitronics default password "1111" used in 2023 attacks. Rockwell factory defaults targeted in 2026 campaign |
Indicators of Compromise
CISA-Listed Attacker IPs (from STIX file)
185.82.73.164
185.82.73.165
185.82.73.167 ← port 44818 open, tagged "ics" in passive scan data
185.82.73.168
185.82.73.170 ← port 44818 + 1801 open
185.82.73.171
135.136.1.133
IOCONTROL Malware (Prior Campaign — 2023/2024)
From the same threat group's earlier operations. The 2023 C2 infrastructure is now seized/dead. No malware sample has been disclosed for the 2026 Rockwell campaign.
Binary Path: /usr/bin/iocontrol
Persistence: /etc/rc3.d/S93InitSystemd.sh
C2 Protocol: MQTT on port 8883
DNS: Cloudflare DoH (1.1.1.1:443)
Encryption: AES-256-CBC
C2 Status: All domains seized/dead. C2 IP still online but reconfigured.
Targeted Ports
20256 — PCOM (Unitronics)
502 — Modbus
2222 — Listed in advisory
102 — S7comm
22 — SSH (Dropbear deployment)
Targeted Devices
Rockwell Automation Micro850
Unitronics Vision V570
Kupferle 9800i-120-A-X-A (claimed)
Orpak fuel management systems
Gasboy payment terminals
Where Continuous Monitoring Makes the Difference
Every stage of this campaign could have been detected earlier with the right monitoring in place. Here is where each layer of continuous intelligence would have made a difference.
The 27 compromised Rockwell employees with ADFS/SSO credentials appeared in stealer log databases before any advisory was published. Continuous dark web monitoring flags these credentials in near-real-time, enabling password resets and session revocation before attackers can use them.
Port 44818 scanning has been trending upward since 2022 — from 1,707 daily records to 4,857 on the day of the advisory. Sensor telemetry shows the shift from Unitronics (port 20256) to Rockwell (port 44818) months before the advisory. Continuous ICS port monitoring catches the reconnaissance phase before exploitation begins.
The 2023 C2 infrastructure (18+ subdomains across 4 countries) was visible in certificate transparency logs months before the first attack. The same principle applies to the 2026 campaign — attackers need infrastructure, and that infrastructure leaves traces. Automated monitoring of certificate issuance, domain registration, and hosting changes catches adversary build-out before operations begin.
APT IRAN posted the Kupferle screenshot to Telegram on March 20, 2026 — 18 days before the CISA advisory. Handala issued their infrastructure threat on April 5. Continuous monitoring of threat actor channels provides early warning of targeting before government advisories are published.
The STIX file containing 8 attacker IPs was available from CISA but initially blocked (HTTP 403). Organizations with automated STIX/TAXII feed ingestion and firewall integration could have blocked these IPs within minutes of the advisory. Those without automated integration may not have them blocked yet.
The Uncomfortable Truth
Over 40,000 U.S. ICS devices are directly accessible from the internet right now. The attackers have proven they can find them, connect to them, and modify their logic. The FBI seized one C2 domain and sanctioned six officers, but the operators remain active and have shifted to new, undisclosed infrastructure targeting American-made Rockwell PLCs.
Meanwhile, the supply chain itself is actively compromised. 27 Rockwell Automation employees have stolen credentials circulating on the dark web — including ADFS single sign-on tokens that could unlock customer deployment databases, firmware distribution systems, and engineering documentation. The individual PLC attacks affect one facility at a time. A supply chain compromise could map every target at once.
The question is not whether they can get in — they already have. The question is whether anyone is watching.
Data Sources
- ICS Port Sensor Telemetry — 4+ years of scanning data across 6 ICS-relevant ports
- Passive Scanning Databases — Live infrastructure verification of 10 IPs (C2 + attacker)
- Certificate Transparency Logs — 93 certificates mapping 18+ C2 subdomains across 4 countries
- WHOIS / Live DNS — FBI seizure confirmation and current C2 domain status
- Dark Web Intelligence Feeds — 200 Rockwell credential leaks, 50+ SCADA attack reports, Kupferle screenshot
- CISA AA26-097A STIX — Government IOCs with 8 attacker IP addresses
- Published Malware Analysis — Full IOCONTROL reverse engineering
- Incident Forensic Reports — Aliquippa Municipal Water Authority analysis
- Malware Hash Databases — IOCONTROL sample verification
Dark Web Monitoring
Continuous surveillance of stealer logs, credential markets, and threat actor channels. Detect compromised credentials before they are weaponized.
Attack Surface Intelligence
ICS/SCADA exposure monitoring, port scanning trend analysis, and internet-facing asset discovery across your infrastructure.
Threat Actor Tracking
Real-time monitoring of APT groups, hacktivist collectives, and ransomware operators targeting your industry and geography.
Certificate Intelligence
Certificate transparency monitoring for C2 infrastructure detection, brand impersonation, and adversary infrastructure mapping.


