
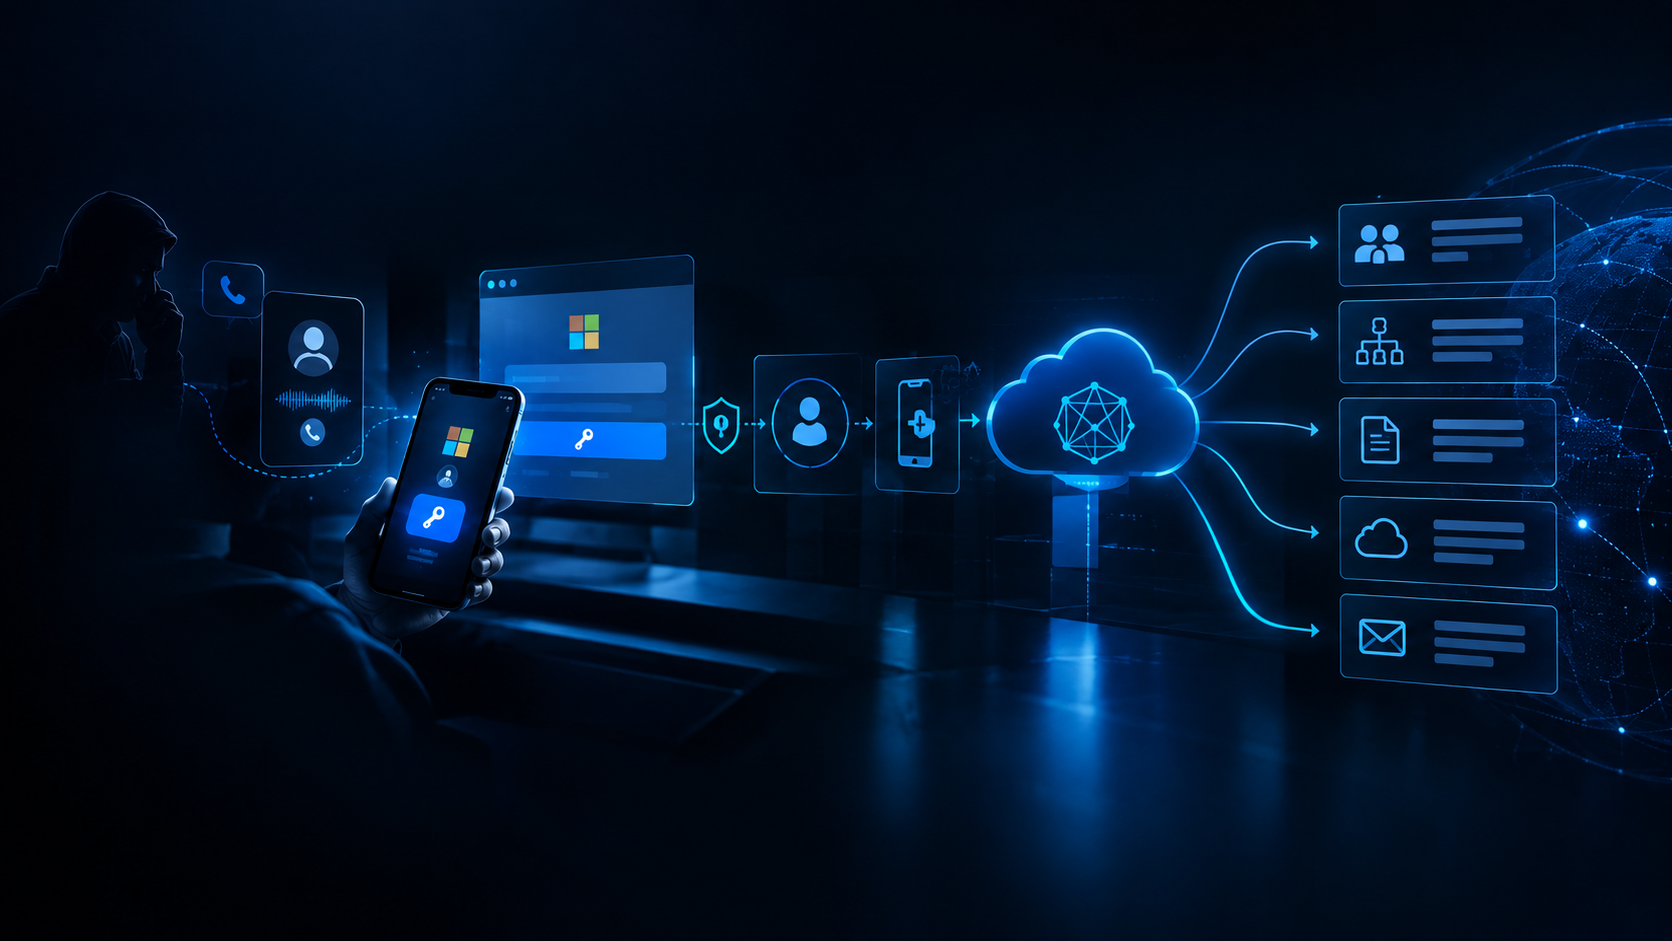
On 9 September 2026, Microsoft Threat Intelligence published an analysis of a social engineering campaign that uses passkey enrolment as a pretext to obtain Microsoft Entra ID sessions. With observed activity dating to no later than April 2026. The intrusions end in scripted collection of SharePoint, OneDrive and Exchange data, followed by extortion.
What follows is the attack chain, the detection signals it produces, where attribution currently stands, and the configuration changes that remove the largest parts of it. It also addresses a question the campaign's framing raises directly: whether passkey authentication was defeated. On the published evidence it was not, and the distinction matters for how organisations respond.
The pretext
The initial contact is a voice call to an employee's personal mobile number, with caller ID spoofed to the organisation's helpdesk line. Microsoft records that the caller asserts that "a passkey, multifactor authentication (MFA), or single sign-on (SSO) configuration must be updated immediately," and an SMS follows containing a link to a lookalike Microsoft sign-in page. In some investigated intrusions the operator spoofed the target's direct manager by name instead of the helpdesk.
The pretext works largely because it is true. Passkey migrations are in progress at many organisations and they are mandatory, so the premise matches what employees have already been told to expect. The enrolment flow is unfamiliar, which makes being talked through it by telephone plausible. And awareness training has spent years positioning passkeys as the phishing-resistant option, so the caller is nominally offering to improve the target's security.
Contact on a personal device places the interaction outside organisational controls entirely. There is no mail gateway involved, no logging, and no artefact available for post-incident review. Independent reporting describes the same script in other campaigns, characterising it as a false pretext of an urgent helpdesk mandate to enable FIDO2 passkeys or update multi-factor authentication enrolment.
Attack chain
From initial contact to exfiltration
Based on Microsoft Threat Intelligence, 9 September 2026, with steps corroborated by independent vendor reporting
- Reconnaissance Employee names, roles and personal mobile numbers collected in advance, together with the organisation's helpdesk number for caller-ID spoofing. T1591 · T1598
- Voice and SMS phishing Helpdesk or manager impersonation on a personal device, asserting an immediate passkey, MFA or SSO configuration change, followed by an SMS containing the link. T1566.004
-
Victim-branded phishing portal
A lookalike Microsoft sign-in page at
companyname.maliciousdomain.com, placing the target organisation's name in the leftmost label of the hostname. T1583.001 - Session capture Either an adversary-in-the-middle proxy relaying the genuine authentication flow and capturing the issued session token, or device-code phishing, in which the operator supplies a code for the victim to enter in their own browser. T1557 · T1528
- MFA method registration A phone number, authenticator application or software OTP token registered on the account, typically within minutes of initial sign-in and from an unmanaged device. The method persists across a password reset. T1556.006
- Directory reconnaissance Users, groups, directory roles, applications and service principals enumerated via Microsoft Graph to identify privilege and locate data. T1087.004 · T1069.003
-
Repository discovery
SharePoint and OneDrive mapped through the sites, drives, search and delta
endpoints, including wildcard and
contentclass:STS_Sitequeries that enumerate all reachable content. T1213.002 - Throttled collection Bulk retrieval of files and mail, held below about 1,000 items an hour and distributed across hours or days. T1530 · T1114 · T1567
Session capture methods
Microsoft states that "the passkey narrative serves as a convincing pretext to guide victims through adversary-in-the-middle (AiTM) phishing or device-code authentication flows." The two routes leave very different evidence behind.
The adversary-in-the-middle route uses a reverse proxy positioned between the victim and the genuine Microsoft login endpoint, forwarding each field and prompt so that the victim completes a real authentication including MFA, while the proxy retains the resulting session cookie. The authentication that Entra ID records is valid in every respect.
Device-code phishing is the method most frequently confirmed as the entry point in independently investigated incidents. The operator initiates a device-code flow and guides the victim through entering the resulting code in their own browser, so authentication completes on the victim's managed, compliant corporate device. No credential is transmitted to the attacker at any point, and nothing is typed into a spoofed page.
The consequence is that device-posture and location conditions in Conditional Access evaluate correctly and permit the sign-in, because the device and location are genuine. Disabling the flow is therefore the highest-impact single mitigation against this entry route.
Device code flow has been blocked by default under security defaults since 1 July 2026, but for new tenants only. Existing tenants retain the flow until it is explicitly disabled. The Conditional Access Authentication flows condition can block device code flow and authentication transfer, scoped broadly with an exception group for legitimate cases such as shared devices, conference room hardware and CLI tooling without a browser.
Persistence and containment
Following initial sign-in, the actor registers an authentication method under their own control. Microsoft records that "the actor enrolled an MFA method under their control, typically by registering a new phone number, authenticator application, or software-based one-time password (OTP) token," describing this as transforming temporary compromise into a durable foothold, and maps it to MITRE T1556.006. Independent incident reporting places the registration within minutes of initial sign-in, originating from the same residential proxy address used to capture the session.
This defeats the standard containment sequence. A password reset leaves the attacker-registered factor in place, allowing re-authentication. Effective containment requires four steps in order:
- Revoke active sessions and refresh tokens. A credential reset alone does not invalidate issued tokens.
- Audit all registered authentication methods on the account against what the user recognises, and remove those that are unrecognised. This must precede the reset, otherwise access is re-established through the remaining method.
- Reset the credential through a verified out-of-band channel, not the helpdesk channel the actor has demonstrated the ability to impersonate.
- Re-enrol authentication under supervision, and check for attacker-registered devices in Entra ID in addition to authentication methods.
Collection activity and detection signals
Collection is scripted. That is the main detection opportunity. Microsoft observed the
python-httpx user agent associated with high-volume SharePoint and OneDrive access. Other
vendors investigating comparable intrusions recorded a different Python HTTP library,
python-requests/2.28.1, and in some cases WindowsPowerShell/5.1 with the client
application identifier spoofed to Microsoft Office while the recorded user agent still identified a
scripting library.
python-httpx and python-requests are distinct libraries producing distinct
user-agent strings. A detection pinned to a single literal value provides limited coverage. The
generalisable signal is any HTTP client library presenting a delegated user token to Graph or SharePoint
at a volume and regularity inconsistent with interactive use.
Two further characteristics reduce visibility. Volume is held below about 1,000 files or messages an hour, which sits beneath common alerting thresholds, and the activity is spread across hours or days instead of arriving in one burst. Access is also often recorded as FileAccessed and not FileDownloaded, so both events need equal weight in detection logic where the user agent identifies a scripting library or the volume exceeds interactive browsing.
Detection signals, roughly in order of value:
- Registration of a new authentication method within one hour of a sign-in flagged as risky, from an unfamiliar device, or from a residential proxy or hosting provider address range.
- Graph reconnaissance spanning three or more categories (directory, privilege, application, repository, mailbox) within a 30-minute window from a single identity.
- Any scripting-library user agent presenting a delegated user token to Graph, SharePoint or Exchange.
- Wildcard or
contentclass:STS_SiteSharePoint search queries, which enumerate all reachable sites and have minimal legitimate interactive use. - Sustained file access from a single identity at a rate that is both elevated and uniform, interactive access being characteristically irregular.
- Device-code authentication events, where the flow has not been disabled.
These detections depend on telemetry that is not enabled by default in all tenants. Graph activity logs and mailbox auditing must be enabled and retained for a period long enough to investigate an intrusion that unfolds over several days.
Attribution
Microsoft's wording is frequently paraphrased inaccurately as naming two groups. The published statement is that the initial access activity "is used by a range of threat actors, including Storm-3121, Storm-3032, and others." Storm-3121's initial access is described as leading to ShinyHunters and Falcon extortion; Storm-3032 is described as a set of actors that splintered from the BlackFile group and now operate under the Helix extortion banner.
Other vendors assessing the same tradecraft have drawn the cluster boundaries differently. The lineage is an assessment, not an established fact.
| Question | Microsoft | Second assessment | Third assessment |
|---|---|---|---|
| Cluster boundaries | A range of actors including Storm-3121 and Storm-3032, assessed as separate clusters | A single actor, tracked as UNC6671, rebranded from BlackFile to REDACT, operating Falcon, Helix and Pink as brands | Reports Helix without asserting a wider cluster |
| ShinyHunters relationship | Storm-3121 initial access leads to ShinyHunters extortion | Assesses the actor as operationally independent of ShinyHunters, having adopted the name for credibility | States that links stop short of confirmed attribution |
| Published evidence | Not published | Shared root domains across brands; identical phishing templates hosted concurrently | Exfiltration IP four addresses from a known BlackFile address on the same ASN, shared registrar, shared tradecraft; notes the ASN evidence is not uniquely attributable |
No published assessment maps the Storm designations to UNC6671, so any equivalence between them is inference, not published assessment. On 7 August 2026, REDACT publicly denied affiliation with Helix and Pink, stating that Falcon is its only affiliate and that former affiliates had replicated its techniques. This is an adversary claim and carries no evidential weight, but indicates the lineage is disputed within the ecosystem as well as between analysts.
For defenders the disagreement matters little. Every published account describes the same playbook, the same infrastructure pattern and the same persistence mechanism. Defend against the technique, which several crews now share, not against a named group.
Infrastructure characteristics
The operators do not provision separate infrastructure per target. They register generic passkey-themed root domains and create a victim-named subdomain for each organisation. Microsoft records that the actor "creates domains following the pattern companyname[.]maliciousdomain[.]com." This is also why a single root domain has been observed serving organisations subsequently extorted under two different brands. The August 2026 infrastructure census identified 63 root domains supporting more than 104 victim subdomains, with the interval between registration and operational use measured in hours.
Published root domains include, defanged:
secure-passkey[.]com        add-passkey[.]com         setupmypasskey[.]com
createssopasskey[.]com      addssopasskey[.]com       myssopasskey[.]com
passkeyhelpdesk[.]com       passkeydeploy[.]com       integratedsso[.]com
oktasession[.]com           oskeysync[.]com           keysyncos[.]com
// served as companyname.<root>
Block them, but do not mistake blocklisting for a control. The domains are disposable, they rotate on a timescale of hours, and published lists are historical by the time anyone consumes them. The durable detection is the structural pattern: a recently registered domain carrying the organisation's own name as a subdomain. Certificate transparency monitoring for organisational brand strings identifies this class of infrastructure during the window in which the activity remains external to the tenant.
Whether passkey authentication was defeated
No reporting in this campaign demonstrates a failure of WebAuthn. Passkeys are bound to the origin for which they were created, so a passkey registered for one domain cannot produce a valid assertion when presented to a lookalike domain. Microsoft's own framing is that the passkey narrative functions as a pretext, not as a defeated control.
Two real weaknesses do exist. Neither is a defect in the standard.
Phishable fallback methods
Where an account can authenticate with either a passkey or a weaker method, an adversary-in-the-middle proxy can modify the page it serves so that the passkey option is not presented, causing the user to authenticate with the phishable fallback. Security researchers documented this technique, termed MFA downgrade, in July 2025 and demonstrated it against Windows Hello for Business and two other major passkey implementations. It was independently reproduced against Entra ID in August 2025 by spoofing a Safari-on-Windows user agent to induce Entra to offer a weaker method. The conclusion is an architectural one. Where a phishing-resistant method exists but a weaker backup method stays registered, the account is still phishable at the level of that weaker method.
Two things qualify the finding. Where an authentication policy enforces phishing resistance, only phishing-resistant methods are accepted and the downgrade attempt is blocked and logged, so the technique applies to configurations that retain a weaker method, which is the majority. The researchers who reproduced it against Entra ID stated in August 2025 that they had not observed downgrade attacks in the wild. No published reporting connects MFA downgrade to the 2026 campaigns described here. The technique has been demonstrated; it has not been observed in this activity, and the two should not be conflated.
Attacker-registered passkeys
Entra ID supports FIDO2 keys and passkeys as standalone passwordless credentials. An actor holding a valid
session can therefore register a key under their own control, after which authentication is possible
without the password or the legitimate device, and the capability survives a credential reset. That is how the product is designed; it is not a defect. Microsoft has constrained the registration step: it requires an ngcmfa claim minted within about 15 minutes, and tenants can restrict which authenticator models are permitted by AAGUID. The practical implication is that registered authentication methods need the same monitoring as credentials.
No published reporting states whether any victim had a passkey registered at the time of compromise. If the affected accounts were authenticating with push notifications or one-time codes, the passkey reference functioned solely as a pretext and the campaign carries no implication for passkey security. This distinction is material to any conclusion drawn about passkey adoption from these incidents, and it is not currently addressed in the published record.
Recommended changes
Ordered by how much of the chain each one removes:
- Block device code flow and authentication transfer in Conditional Access, with a narrow exception group. This removes the entry method most frequently confirmed in these intrusions, and existing tenants are not covered by the July 2026 default.
- Enforce phishing-resistant authentication and remove fallback methods. Deploying passkeys while retaining SMS, voice or OTP registration for the same accounts leaves the downgrade path available. Prioritise privileged roles and finance functions.
- Treat authentication method changes as security events and alert on every registration, not only those on privileged accounts. This is a low-cost detection covering the step that converts a stolen session into a persistent intrusion.
- Strengthen helpdesk identity verification in both directions. Verify callers through a channel the caller did not select, and publish an internal standard that the helpdesk will not telephone staff to guide them through authentication changes, so that the pretext is itself anomalous.
- Require managed, compliant devices for Exchange, SharePoint and Graph-privileged applications. This constrains but does not eliminate device-code phishing, which completes on the victim's compliant device.
- Restrict user consent for applications, requiring administrative approval for
high-privilege Graph permissions including
Mail.Read,Files.Read.AllandDirectory.Read.All. - Limit unmanaged device sessions to web-only access with downloads blocked, and disable anonymous sharing links in SharePoint and OneDrive.
- Enable Graph activity logs and mailbox auditing, with retention sufficient to investigate multi-day intrusions.
- Monitor certificate transparency for organisational brand strings to identify victim-named subdomains prior to use.
- Update awareness training for this pretext. Existing training addresses credential phishing by email; it does not typically address telephone contact regarding a passkey or MFA migration.
Where compromise is suspected, revoke sessions and refresh tokens before resetting credentials, audit all registered authentication methods on affected accounts, and retrieve Graph and mailbox audit logs for the full suspected window and not just the last few hours, as collection in these cases extends across days. TechOwl's identity compromise response team can be contacted through the contact page.
Sources
- Microsoft Threat Intelligence, "Passkey-themed social engineering leads to identity and cloud compromise" (9 September 2026), the primary source for the attack chain, the T1556.006 mapping, the
companyname[.]maliciousdomain[.]compattern and thepython-httpxobservation. - MITRE ATT&CK T1556.006, Modify Authentication Process: Multi-Factor Authentication.
- Corroborating detail on device-code entry, MFA registration timing, infrastructure census figures, extortion payments, cluster attribution and MFA downgrade research is drawn from four further vendor threat intelligence publications issued between July 2025 and August 2026. All are first-party vendor reporting and none has been reproduced by a neutral party. Attribution in particular is an assessment, not a confirmed fact.


